io.github.l33tdawg/sage MCP Server
io.github.l33tdawg/sage
Persistent, consensus-validated institutional memory for AI agents with Byzantine-resilient infrastructure.
What is the io.github.l33tdawg/sage MCP server?
(S)AGE is a sovereign agent memory infrastructure that gives AI agents persistent, consensus-validated institutional memory across conversations. It runs locally using CometBFT consensus, confidence scoring, and natural decay, providing a foundation for multi-agent systems rather than a simple vector database.
SAGE provides institutional memory infrastructure for AI agents that persists across conversations and is validated through Byzantine Fault Tolerant consensus. Unlike flat-file or vector-database approaches, it uses distributed ledger primitives to ensure memory integrity, includes confidence scoring and natural decay, and supports both single-agent and multi-agent network deployments. The CEREBRUM dashboard offers real-time visualization and management of agent memories, federation, and system health.
How to install io.github.l33tdawg/sage
Copy-paste configuration for popular MCP clients.
Tools & capabilities
Tools this server exposes to the agent.
sage_inbox— Retrieve pending and claimed work messages for agents, with support for exact-recipient local canonical messages and durable wake generation.sage_timeline— Query agent memories within a bounded 31-day range with deterministic ordering and filtering.Memory Auto-Voter— Deduplication, quality assessment, and consistency validation for memory writes with per-node signed voting.Governance Engine— On-chain validator proposals and voting for multi-agent network management.CEREBRUM Dashboard— Web-based operator console at localhost:8080/ui with 3D MRI brain visualization, chain health monitoring, agent management, federation controls, and recall tuning.Network Agent Manager— Add/remove agents, manage key rotation, and configure LAN pairing for multi-agent deployments.Encryption— Optional AES-256-GCM encryption for SQLite storage with vault recovery controls.
Use cases
- Build multi-agent systems with persistent, consensus-validated shared memory across conversations
- Monitor agent network health and memory integrity through the CEREBRUM 3D brain dashboard
- Federate multiple SAGE instances for distributed agent collaboration with Byzantine fault tolerance
- Manage agent identities, permissions, and key rotation in production deployments
- Tune memory recall depth and reranking for optimized agent decision-making
- Import/export and recover agent memories with encryption controls
io.github.l33tdawg/sage MCP server FAQ
(S)AGE is institutional memory infrastructure built on Byzantine Fault Tolerant consensus (CometBFT), not a vector database. It provides persistent, consensus-validated memory with confidence scores and natural decay, supporting both single-agent and multi-agent networks. Every memory write goes through pre-validation, signed voting, and BFT quorum before committing.
Yes, (S)AGE is open-source and available for download. It runs locally as a standalone application or as a containerized service (ghcr.io/l33tdawg/sage).
(S)AGE is available as an MCP server. Download the binary from https://l33tdawg.github.io/sage/ (double-click to run), or use the container image ghcr.io/l33tdawg/sage:11.23.11. It works with any AI agent via MCP or REST APIs.
(S)AGE runs locally and does not require external API keys. For multi-agent deployments, it includes built-in key rotation, domain permissions, and RBAC controls managed through the CEREBRUM dashboard.
Yes, (S)AGE supports multi-agent deployments with federation, direct and secure relay modes, and independent read/copy choices. Each agent node votes with its own consensus key in the same BFT pipeline.
(S)AGE uses SQLite by default with optional AES-256-GCM encryption, and also supports PostgreSQL for production deployments.
README (reference)
Source of truth, from the repository.
(S)AGE — Sovereign Agent Governed Experience
Persistent, consensus-validated memory infrastructure for AI agents.
SAGE gives AI agents institutional memory that persists across conversations, goes through BFT consensus validation, carries confidence scores, and decays naturally over time. Not a flat file. Not a vector DB bolted onto a chat app. Infrastructure — built on the same consensus primitives as distributed ledgers.
The architecture is described in Paper 1: Agent Memory Infrastructure.
<a href="https://glama.ai/mcp/servers/l33tdawg/s-age"> <img width="380" height="200" src="https://glama.ai/mcp/servers/l33tdawg/s-age/badge" alt="(S)AGE MCP server" /> </a>Just want to install it? Download here — double-click, done. Works with any AI.
Architecture
Agent (Claude, ChatGPT, DeepSeek, Gemini, etc.)
  │ MCP / REST
  ▼
sage-gui
  ├── ABCI App (validation, confidence, decay, Ed25519 sigs)
  ├── Memory Auto-Voter (dedup, quality, consistency — one vote per node, signed with the node's consensus key)
  ├── Governance Engine (on-chain validator proposals + voting)
  ├── CometBFT consensus (single-validator or multi-agent network)
  ├── SQLite + optional AES-256-GCM encryption
  ├── CEREBRUM Dashboard (SPA, real-time SSE)
  └── Network Agent Manager (add/remove agents, key rotation, LAN pairing)
Personal mode runs a real CometBFT node with a per-node memory auto-voter — every memory write goes through pre-validation, a signed vote transaction, and the BFT quorum before committing. One node casts one vote; add more agents from the dashboard and each node votes with its own key, exactly the same consensus pipeline as a multi-node deployment.
Full deployment guide (multi-agent networks, RBAC, federation, monitoring): Architecture docs
CEREBRUM Dashboard
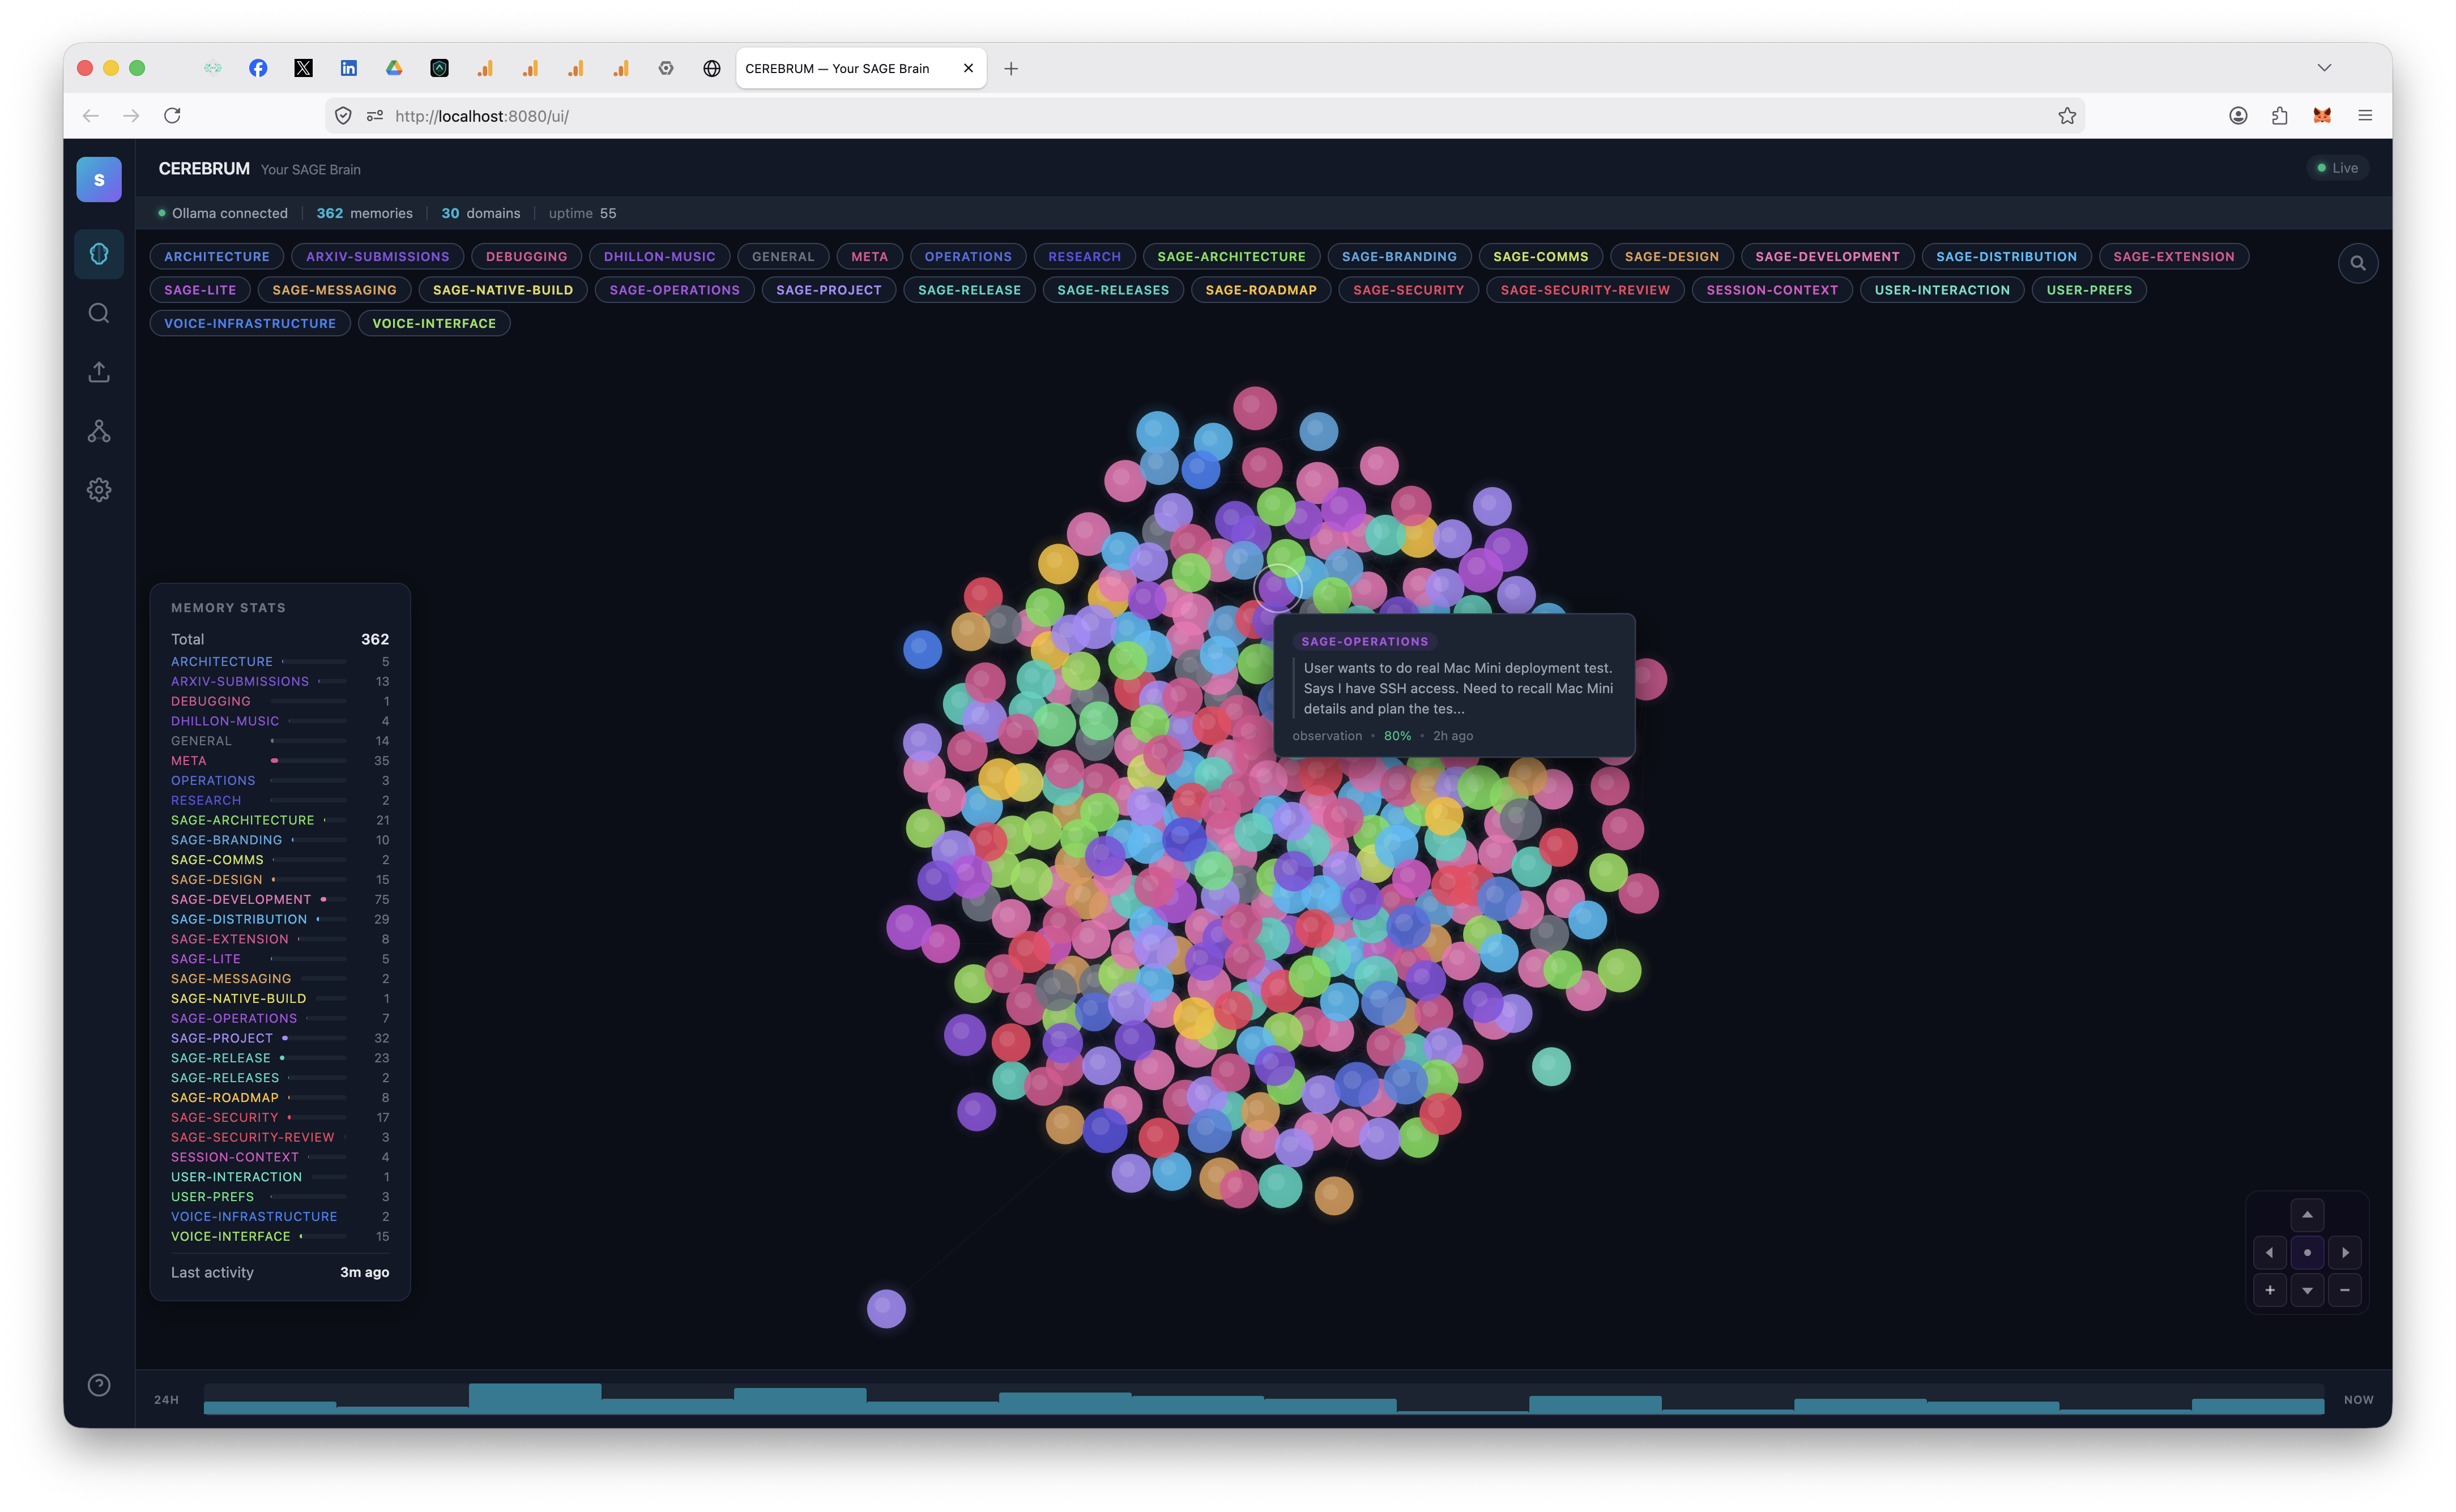
http://localhost:8080/ui/ — a dashboard-native operator console centered on the 3D MRI memory brain, with chain health, agents, federation, semantic memory, recall tuning, vault recovery, tasks, imports, and updates around it. Every major workflow is available from the browser; the CLI stays there for automation and recovery.
| Control Board | Federation | Recall Engine |
|---|---|---|
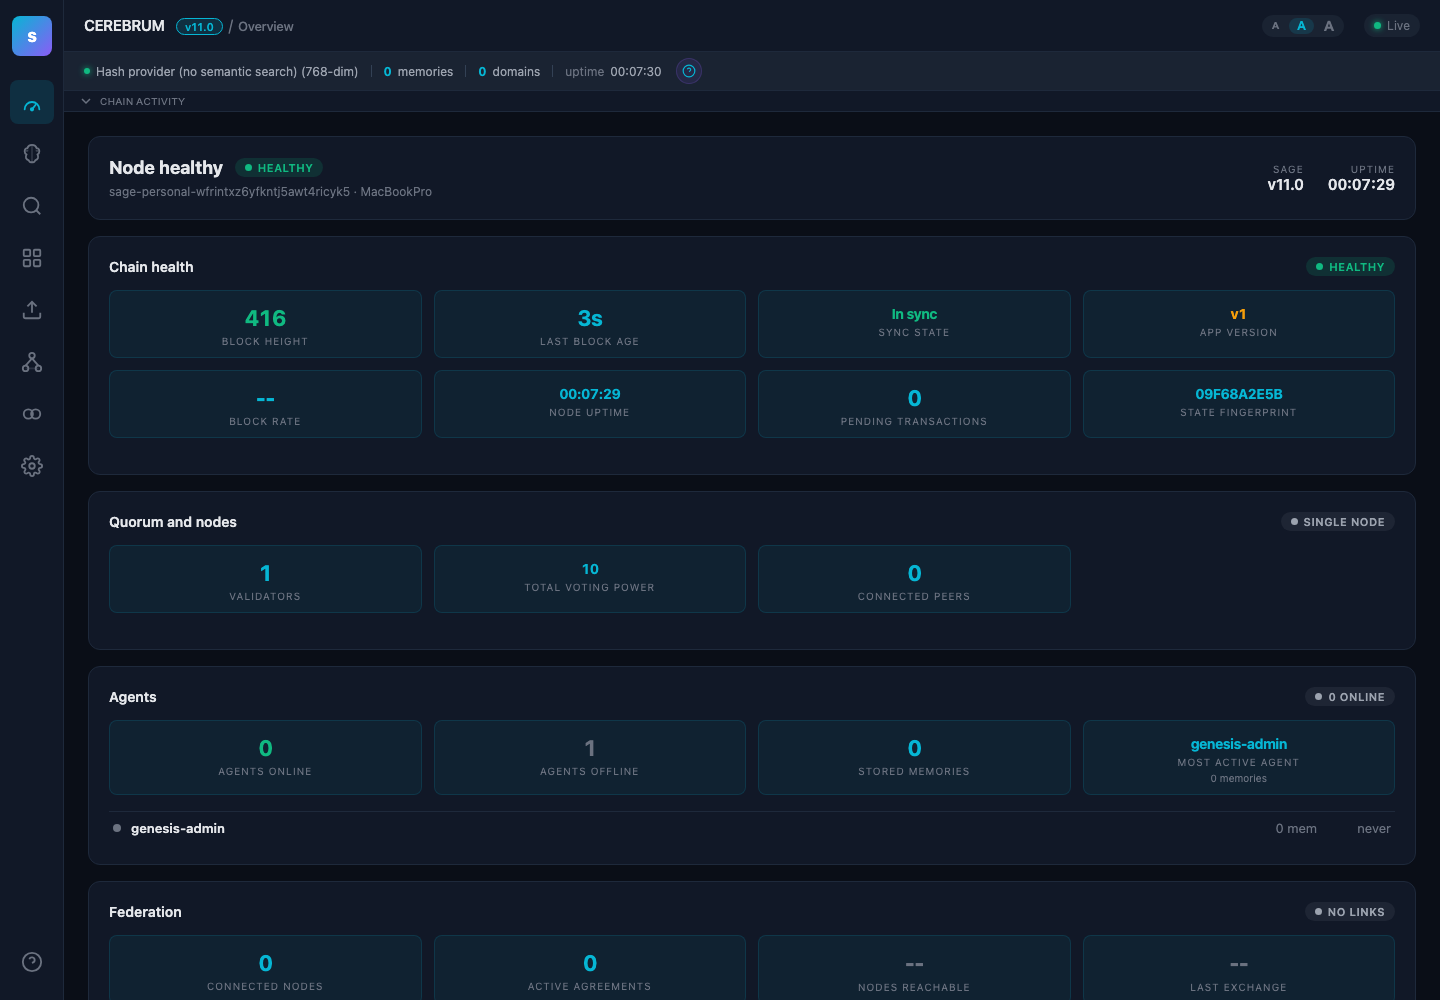 | 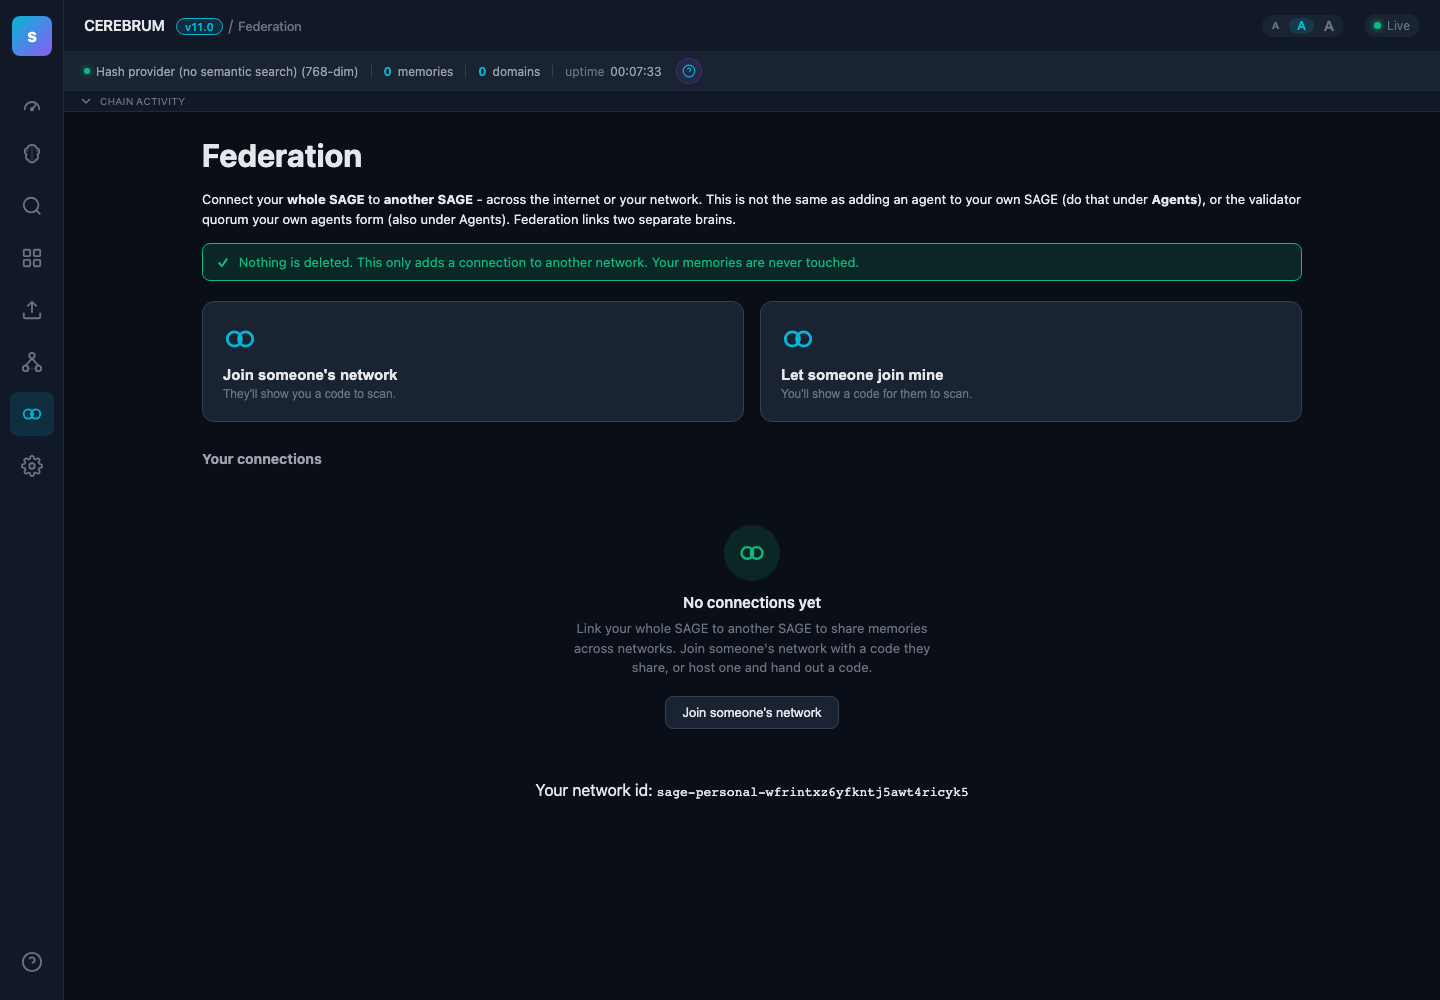 | 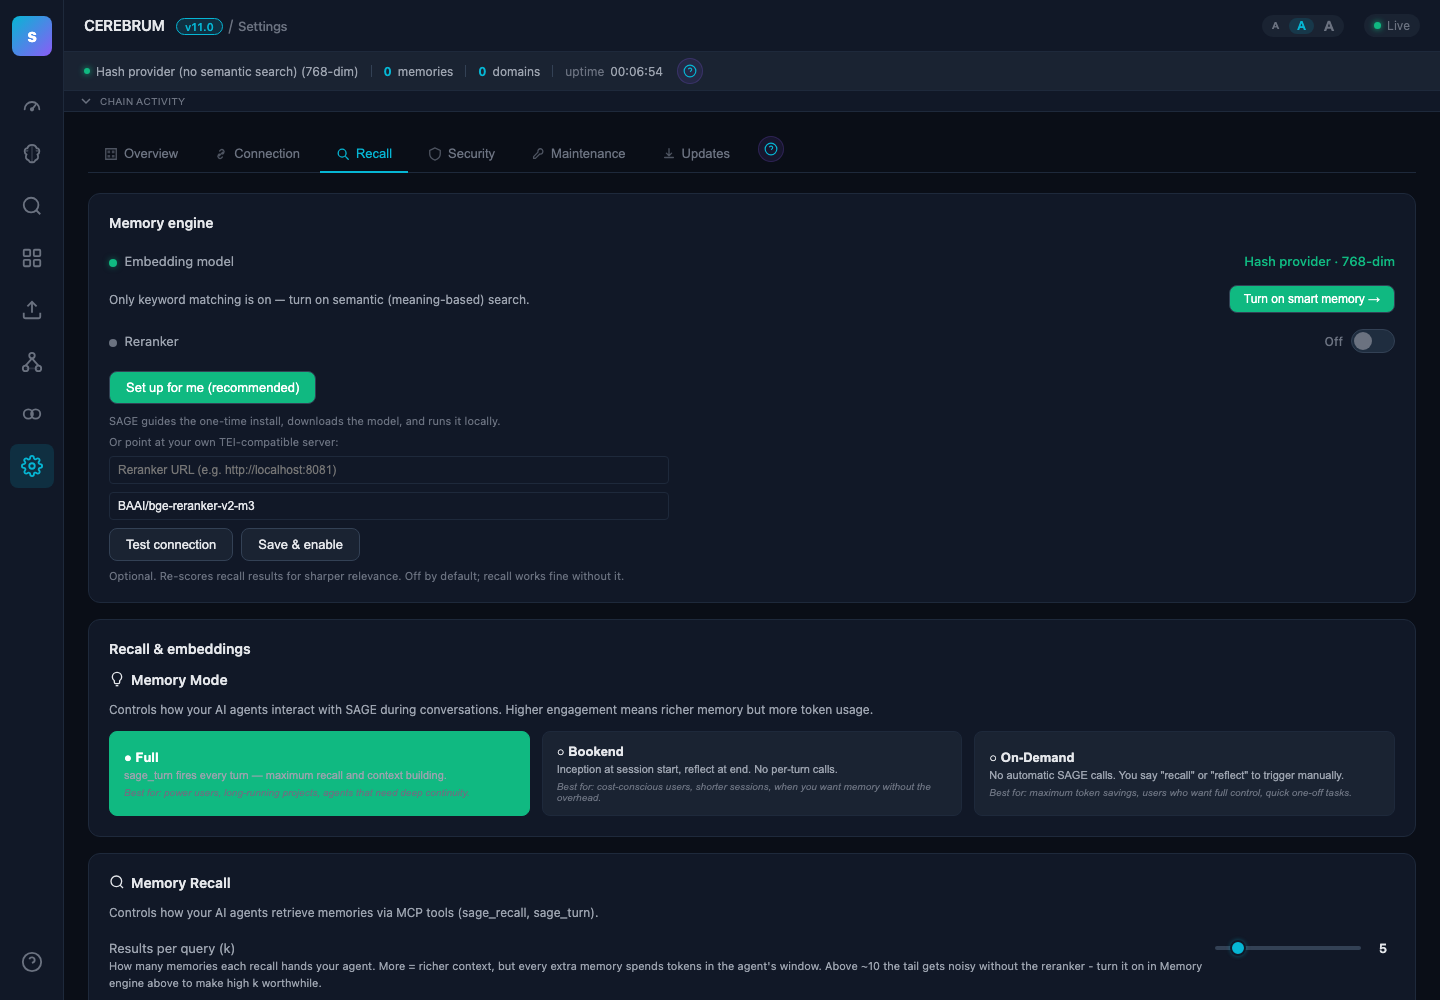 |
| Chain health, quorum, agents, federation, and embeddings | One trust-only JOIN that prepares Direct and Secure relay automatically, followed by independent Read/Copy choices on each SAGE | Smart-memory setup, managed reranker install, and recall-depth tuning |
The dashboard also includes agent management, domain permissions, key rotation, import/export, software updates, and encryption controls.
What's New in v11.18.22
A missing optional ForceGraph API can no longer strand CEREBRUM after the
verified brain has rendered. The renderer now publishes the core graph and
truthful counts before optional anatomical, control, and interaction setup. The
bundled runtime's absent clickAfterDrag helper is feature-gated, so the brain
hull, controls, and auto-rotation continue instead of falling into the cold
unavailable path with real nodes already on screen.
This patch introduces no new consensus application version or state migration. The ceiling remains app-v26; v11.18.22 introduces no app-v27.
Container: ghcr.io/l33tdawg/sage:11.18.22. SDK 11.18.22.
What's New in v11.18.21
A domain-summary refresh can no longer cover a verified MRI graph. The MRI renderer is now the sole authority for the central unavailable overlay. Domain inventory failures stay localized to their own retrying panel, while genuine cold graph failures and unsafe mode switches remain fail-closed.
This patch introduces no new consensus application version or state migration. The ceiling remains app-v26; v11.18.21 introduces no app-v27.
Container: ghcr.io/l33tdawg/sage:11.18.21. SDK 11.18.21.
What's New in v11.18.20
A transient MRI refresh no longer hides a graph CEREBRUM has already verified. Memory and Connectome snapshots now retain their explicit source mode. If a live refresh fails, CEREBRUM keeps the last verified snapshot visible only when it belongs to that same mode, while retrying in the background. Cold failures and failed mode switches still fail closed, so Connectome bytes can never masquerade as a verified memory projection.
This patch introduces no new consensus application version or state migration. The ceiling remains app-v26; v11.18.20 introduces no app-v27.
Container: ghcr.io/l33tdawg/sage:11.18.20. SDK 11.18.20.
What's New in v11.18.19
Codex project hooks stay inside their project. The v11.18.18 byte-exact
self-healer could mistake Codex's user-global ~/.codex configuration directory
for a project and generate a global hooks.json. That made an unrelated Codex
task receive SAGE inbox Stop nudges for the shared agent identity. The healer now
refuses the user-home/global scope; project-local hooks continue to self-repair.
Connectome clicks now have one hit-tested owner. The redundant DOM click fallback that raced ForceGraph's deferred node click is gone. Small pointer wobble is handled by one explicit tolerance, background dismissal uses the graph's raycast result, and clicking a second neuron no longer closes the inspector and starts a competing zoom-out first. Raw domain-access metadata is summarized behind a bounded disclosure below traffic, relationships, and memory details; bloomed memory nodes now expose hover and accessible click feedback.
This patch introduces no new consensus application version or state migration. The ceiling remains app-v26; v11.18.19 introduces no app-v27.
Container: ghcr.io/l33tdawg/sage:11.18.19. SDK 11.18.19.
What's New in v11.18.18
Codex upgrades now repair stale SAGE lifecycle hooks automatically. On
every MCP startup, the project self-healer compares all five installer-owned
Codex hook scripts with their fully rendered current templates. A mixed
generation can no longer pass merely because the files exist or another hook
mentions the current binary. Upgrading therefore replaces legacy no-op Stop
hooks and malformed prompt hooks without requiring a second manual
sage-gui codex install run.
The CEREBRUM Connectome now leads with the graph itself. Neurons have a larger practical click target; clicking one opens its persistent identity, visible incoming/outgoing traffic, strongest peer, directed connection list, and visible memory lobe. The compact fallback selector now shows only agents with visible peer relationships, ordered by retained traffic, instead of turning a large dormant/test roster into the primary navigation surface. Isolated authorized neurons remain visible and clickable in the brain and join the selector while selected.
This patch introduces no new consensus application version or state migration. The ceiling remains app-v26; v11.18.18 introduces no app-v27.
Container: ghcr.io/l33tdawg/sage:11.18.18. SDK 11.18.18.
What's New in v11.18.17
Routine MCP restarts no longer make the same stdio agent disown its own
unfinished messages. The primary stdio runtime now persists one opaque
claimant identity per exact signed agent, provider, and project under
SAGE_HOME, and holds an OS advisory lock as the liveness fence. A later
runtime reuses that identity only after the earlier process is no longer live;
a genuinely concurrent runtime receives an independent identity and retains
the existing one-handler and compare-and-swap handoff boundary. In-place
installed-binary handoff also carries the current claimant identity while the
old process keeps the lock alive.
The fix is deliberately prospective and does not bulk-transfer historical
claims created by pre-v11.18.17 random process identities. Those rows remain
visible through claimed_elsewhere_count and passive history and can still be
transferred one at a time with the existing CAS-fenced handoff after the old
claimant is known dead. HTTP MCP conversations remain transport-scoped. This
patch introduces no new consensus application version or state migration. The
ceiling remains app-v26; v11.18.17 introduces no app-v27.
Container: ghcr.io/l33tdawg/sage:11.18.17. SDK 11.18.17.
What's New in v11.18.16
Claimed agent work no longer disappears from the inbox that claimed it.
sage_inbox now returns a separate bounded own_claimed_unfinished projection
for messages already owned by the exact current agent session. The projection
is passive: it never claims, refreshes, transfers, or duplicates work, and it
does not change the established items or count meaning of newly available
work. Exact agent/session filtering, completion and expiry handling, bounded
results with an exact total, reply-after-repoll, and nonmutation are pinned by
store, REST, and MCP regression coverage.
The payload-free hook status path also checks the durable wake snapshot, so
claimed-but-unfinished work cannot be reported as a clean inbox merely because
no unclaimed row remains. Older or temporarily incapable nodes degrade to an
explicit unavailable state instead of either a false zero or a failed primary
inbox call. This patch does not automatically transfer claims from another
session; passive history plus explicit compare-and-swap handoff remain the
recovery boundary. It introduces no new consensus application version or state
migration. The ceiling remains app-v26; v11.18.16 introduces no app-v27.
Container: ghcr.io/l33tdawg/sage:11.18.16. SDK 11.18.16.
What's New in v11.18.15
Every unfinished exact-recipient local canonical message now has a durable
wake generation, including upgrade-era claimed-only work and sends through the
deprecated pipe route. Startup backfill covers both pending and claimed rows, so a recipient
whose only live work was already claimed cannot reopen as the silent
{seq:0,pending:true} state. Keyed exact-local pipe sends use the canonical
idempotent admission path; unkeyed sends insert the row and advance the same
recipient sequence atomically. Publication happens only after commit, exact
replays do not republish, and an incapable backend fails before insertion rather
than creating durable work that wake consumers cannot observe as new.
The experimental Claude notification adapter is explicitly opt-in again. The
shipped Claude Code host does not consume that custom notification, while the
adapter would otherwise acquire the one exact-agent wake lease and exclude a
useful long-running consumer. SAGE_CLAUDE_CHANNEL=true still enables it for an
operator who intentionally has a compatible host.
Pending-memory presentation is deterministic even when creation timestamps tie:
SQLite and PostgreSQL both use memory_id as the final ordering key. The
documentation citation guard now parses newline-separated and hyphenated paths,
pins every concrete declaration/lead/interior anchor, repairs only explicitly
accepted declaration anchors, refuses semantic locations it cannot reconstruct,
and inventories the remaining legacy skipped and bare references. This patch
introduces no new consensus application version or state migration. The ceiling
remains app-v26; v11.18.15 introduces no app-v27.
Container: ghcr.io/l33tdawg/sage:11.18.15. SDK 11.18.15.
What's New in v11.18.14
Durable agent messages now stay visible until the work is actually
finished. Claiming a message no longer makes the payload-free wake surface go
quiet: both pending and claimed rows remain unfinished, a reconnect at the
current cursor receives an immediate wake, and sage_inbox reports an exact
payload-free claimed-elsewhere state instead of a bounded-scan false zero.
Claude Code project sessions arm the signed wake channel by default, while the
optional Stop hook reads a lease-free monotonic snapshot so new or stranded
work can nudge a session once without stealing the live SSE consumer lease.
The same recovery path is honest at its edges. A claimant-session fence rejection remains a typed conflict instead of masquerading as a missing message, and history plus explicit compare-and-swap handoff remain the only way to recover another session's claim. Canonical retention migration now rescues only the exact historical 24-hour stamp, preserving a sender's chosen bounded TTL across every store reopen, including RFC3339 nanosecond timestamps.
CEREBRUM's Connectome now identifies the agents it renders. Hover details are positioned and escaped reliably, while click, tap, and keyboard selection open one persistent inspector with exact agent identity, visible retained traffic, peers, activity, and an independently loading visible-memory lobe. Selection survives authorized live refreshes, error and empty states stay truthful, mobile uses a bounded sheet, and reduced-motion and established Connectome guidance remain intact.
Agent-as-lobe corroborator reads now use one deterministically ordered bounded
batch instead of an N+1 query pattern, with matching SQLite and PostgreSQL
ordering. The MCP contract also states the server-enforced 31-day
sage_timeline range rather than advertising requests the server rejects.
This patch introduces no new consensus application version or state migration.
The ceiling remains app-v26; v11.18.14 introduces no app-v27.
Container: ghcr.io/l33tdawg/sage:11.18.14. SDK 11.18.14.
What's New in v11.18.13
Hubanov's distributed-engram contribution now connects memories to the neurons that corroborated them. CEREBRUM keeps agent and memory identities in separate graph namespaces, rejects stale bloom generations, and removes every transient bridge on focus or graph replacement. The server uses a deterministic, indexed 96-row evidence prefix and exposes at most 12 authorized bridges without turning historical corroboration into a claim of current possession.
Claude's production wake source can now arm the payload-free message bus.
When explicitly enabled with SAGE_CLAUDE_CHANNEL, the MCP runtime consumes the
existing signed SSE wake route with a random process lease and resumable cursor.
Delivery applies backpressure instead of dropping the newest wake, and shutdown
releases saturated readers without leaking goroutines or claiming message
content.
The Connectome no longer floats an instructional card over the brain. Its guidance lives in the existing reading panel, the mode toggle keeps one stable name and visible pressed state in both themes, keyboard focus remains clear, mobile Reset behavior stays intentional, and view changes are announced to assistive technology.
This patch also closes a claimant-session compatibility bypass: a current typed 404 is authoritative, the deprecated pipe-result alias carries the active MCP session, and only a genuine old-node route miss may fall back. It introduces no new consensus application version or state migration. The ceiling remains app-v26; v11.18.13 introduces no app-v27.
Container: ghcr.io/l33tdawg/sage:11.18.13. SDK 11.18.13.
What's New in v11.18.12
CEREBRUM can now open an agent as a memory lobe. Selecting a connectome neuron lazily blooms that agent's highest-confidence visible memories as engrams, while retaining the operator-only route and app-v23 per-record projection checks. The indexed, bounded query avoids whole-brain scans; stale, failed, and disposed frontend requests cannot leave another agent's lobe on screen.
Dashboard live activity is now guarded as one exact 20-event registry. The seven previously unwired operator events now reach the existing dashboard SSE stream, while message wake, MCP, and wizard protocols stay route-local. A fail-closed typed control-flow audit and executable browser contract reject dead, aliased, escaped, build-tagged, or decoy event sinks.
Signed task creation and message attribution now agree end to end. Every
official task constructor explicitly signs the required initial planned
status, and REST fails fast instead of mutating an omitted signed field into a
transaction that app-v23 through app-v26 must reject. Authorized message and
pipe responses retain exact immutable agent IDs alongside mutable presentation
labels, use one bounded batch metadata query on healthy production stores with
a bounded exact-ID fallback, suppress foreign-chain label collisions, and keep
count-only responses identity-free.
This patch also repairs release-facing documentation drift, pins the current 33-tool MCP inventory, and adds fail-closed symbol/citation coverage for the references it can verify. It introduces no new consensus application version or state migration. The ceiling remains app-v26; v11.18.12 introduces no app-v27.
Container: ghcr.io/l33tdawg/sage:11.18.12. SDK 11.18.12.
What's New in v11.18.11
The CEREBRUM connectome now fires live without widening its operator-only boundary. Successful local message sends emit a contentless invalidation tick; the browser then refetches the existing caller-filtered snapshot and pulses only newly observed synapses. Monotonic generations preserve later ticks across in-flight requests, ordinary reloads, failures, and retries, while initial loads and unrelated refreshes never create false activity.
Dashboard retrieval activity no longer duplicates authorized memory plaintext into the global operator stream. Recall, search, and hybrid events now expose only their event type and result count. The obsolete expandable plaintext panel is gone, and serialized-frame regressions pin the contentless contract and live, non-replayed delivery.
Claude bookend sessions can discover waiting SAGE messages without claiming or revealing them. A signed, payload-free inbox-status hook reports only the current identity and unread count, makes failures visible, preserves unrelated user hooks during self-heal, and exposes the read-only message tools needed to perform the explicit inbox fetch.
This patch also keys local connectome locality by chain identity, removes a stale app-v7 validator warning after app-v14, dims the connectome skull for legibility, requires patched Go 1.25.13 throughout current builders and CI, and publishes checksum sidecars for Windows executables. It introduces no new consensus application version or state migration. The ceiling remains app-v26; v11.18.11 introduces no app-v27.
Container: ghcr.io/l33tdawg/sage:11.18.11. SDK 11.18.11.
What's New in v11.18.10
Multiple MCP runtimes sharing one agent identity can no longer silently lose track of claimed messages. Every MCP conversation now has an opaque claimant session ID. Atomic inbox claims persist that session in passive history, an explicit compare-and-swap handoff transfers work between runtimes, and a stale former owner is rejected if it tries to reply after ownership moved. Receive tokens remain replay-safe after a lost response, while legacy direct REST clients retain their existing agent-level compatibility path.
CEREBRUM can render the agent message bus as a live connectome inside the 3D brain. Registered agents become domain-coloured neurons, directed channels become traffic-weighted synapses, and hub agents settle toward the core. The view consumes the existing RBAC-filtered synapse projection, drops ghost edges, and fences asynchronous mode switches so a slow memory response can never be displayed as connectome data.
Upgrade-watchdog submissions can no longer hold a signing key's nonce lease for the process lifetime when CometBFT wedges. One bounded context now covers both lease acquisition and the broadcast. A deadline after submission remains a typed indeterminate outcome, so the exact signer and bytes stay fenced until their fate is reconciled; elapsed time never releases the key fail-open.
This patch introduces no new consensus application version or state migration. The ceiling remains app-v26; v11.18.10 introduces no app-v27.
Container: ghcr.io/l33tdawg/sage:11.18.10. SDK 11.18.10.
What's New in v11.18.9
Ambiguous CometBFT commit and sync outcomes are now typed at the shared
broadcaster boundary. Transport, status, RPC, decode, shape, hash-binding, and
missing-height failures return ErrSubmitIndeterminate for valid signing keys,
while the existing live-registration path remains an independent fence
backstop. Pre-send request-construction failures remain definitive and do not
fence a key over bytes that never reached a transport.
Federation sync now fails closed if its commit broadcaster ever violates its
contract by returning neither a result nor an error. The exact signer and
encoded transaction remain fenced until reconciliation proves their fate,
instead of releasing the key for a potentially in-flight transaction. A new
cross-package decoder contract also pins the HTTP prologue shared by
internal/tx and the CEREBRUM web path while recording their deliberate verdict
and envelope-tolerance differences.
This patch introduces no new consensus application version or state migration. The ceiling remains app-v26; v11.18.9 introduces no app-v27.
Container: ghcr.io/l33tdawg/sage:11.18.9. SDK 11.18.9.
What's New in v11.18.8
CometBFT transaction submissions no longer permit Go's HTTP transport to transparently redeliver a fenced request after a reused connection fails while reading the response. Commit, sync, byte-identical nonce-fence reconciliation, and CEREBRUM submission paths now share a non-reusing HTTP/1.1 transport seam. Each submission call writes its transaction on one connection and returns an indeterminate result instead of silently delivering the same signed bytes to a second responder. Restart failure reporting also preserves the signer-fence veto ahead of a generic drain timeout.
MCP reply polling now fails safe when a caller presents an unsafe forward
watermark. If reply_since is later than the authoritative retained-reply
head, or no head exists to validate it, sage_inbox returns the newest passive
reply page for deduplication instead of filtering a formal reply into a false
empty result. Complete recovered pages become a new safe baseline; truncated
pages require composite-cursor catch-up, and failed page reads never claim
recovery. A successful outbound sage_message_send also performs one bounded,
sender-exact passive inbox snapshot so an inbound message that arrived after an
earlier empty poll is surfaced during continued coordination.
This patch introduces no new consensus application version or state migration. The ceiling remains app-v26; v11.18.8 introduces no app-v27.
Container: ghcr.io/l33tdawg/sage:11.18.8. SDK 11.18.8.
What's New in v11.18.7
Large signed transactions now use a bounded CometBFT transport instead of
overflowing request headers. Existing smaller broadcasts keep the established
GET wire shape, while large commit, sync, and byte-identical nonce-fence
reconciliation requests use JSON-RPC POST with base64 transaction bytes. Client
transaction and JSON-RPC body limits are independently range-checked, capped at
8,000,000 bytes, and refuse an oversized request before send. Operators raising
them must configure matching CometBFT limits. Independently, every validator
enforces a 1,200,000-byte aggregate raw-transaction budget for app-v20 atomic
finalization, sufficient for the measured 1,304-entry SkillRegistry transaction.
Memory content remains bounded at 512 KiB, while the canonical signed
AgentRequest proof has its own 600,000-byte consensus bound, admitting the
measured 573,723-byte proof without widening the content or aggregate limits.
Response handling accepts strict quoted or numeric int64 heights, rejects
fractional, exponent, null, malformed, and out-of-range heights, and refuses
unsupported content types.
Federation route refresh no longer risks recursively acquiring the sync-policy read lease from a peer-request caller. Opportunistic refresh admission is policy-free and bounded to one pending refresh per peer; the agreement and binding lookup runs asynchronously after the request caller can release its lease. Failed-request and successful-Direct triggers remain covered, while the route-exchange endpoint does not self-trigger refresh.
P2P-only peers can recover when their stored route snapshot is missing or
belongs to an older trust generation. Only the authenticated
/fed/v1/p2p/routes bootstrap exchange may use stale or current route addresses
as connection hints; the current agreement's pinned mTLS identity remains
authoritative. Protected requests reject missing or cross-generation snapshots
with trust_generation_mismatch. A matching-generation empty target set remains
explicitly pinned and cannot fall back to current configuration.
Federation diagnostics now give security evidence precedence over route
availability evidence. Mixed route-availability plus certificate, SPKI, pin,
identity-mismatch, or security-block evidence is classified as
security_blocked; revocation, expired or unknown agreement, trust-failure, or
authentication evidence is classified as trust_failure. Both verdict classes
outrank route availability.
This patch introduces no new consensus application version or state migration. The ceiling remains app-v26; v11.18.7 introduces no app-v27.
Container: ghcr.io/l33tdawg/sage:11.18.7. SDK 11.18.7.
What's New in v11.18.6
Updater snapshots now prove both supported CometBFT layouts before they are
published or reused. Application Badger and persisted consensus state must
match at height H and agree on the application hash. A blockstore committed
through H is accepted only after its H block ID and seen commit match that
state. If the blockstore is durably one block ahead at H+1, SAGE additionally
verifies the complete block and part identity, direct-parent and state-derived
header fields, last and seen commits, validator signatures, and CometBFT's
replay-time block validation. Regression coverage restores the candidate and
runs the real CometBFT handshaker, proving exactly one replayed block and safe
restart reuse. Malformed or more-than-one-ahead provenance is rejected, and an
invalid prior publication is quarantined before a valid replacement can be
published. Cancellation always blocks executable updater handoff, although a
safe snapshot may already have been atomically published. Non-empty H+1
evidence is retryable until application and state catch up.
Federation Retry now performs one bounded, exact-generation recovery
workflow. Concurrent operator clicks share the same route refresh and
authenticated status probe. Direct and relay targets are frozen to the active
JOIN generation, HTTP 401/403 and certificate/identity failures stop before
re-probing, and a revoke or re-pair during the response invalidates the result.
Typed dashboard diagnostics distinguish missing or expired route bundles,
stale Direct routes, unavailable relays, trust-generation changes, and legacy
connections that must be paired again. Ordinary polling and mutating requests
do not enter this retry path.
Memory-reassignment audit failures no longer place request-controlled agent IDs in logs. The source and target are represented by fixed 96-bit truncated SHA-256 fingerprints (24 lowercase hexadecimal characters), preserving stable incident correlation without allowing CR/LF or other control characters to forge log records.
This patch does not change consensus state or application activation. The ceiling remains app-v26; v11.18.6 introduces no app-v27. The signer fence also remains process-local: unresolved submissions still require proof of fate, and crash/restart or a separate signing process is not claimed safe until durable cross-process pre-broadcast intent exists.
Container: ghcr.io/l33tdawg/sage:11.18.6. SDK 11.18.6.
What's New in v11.18.5
Long-lived stdio MCP sessions now follow an installed SAGE upgrade without
executing a request under stale tools. The MCP process snapshots the exact
executable that started it. If the app bundle or binary is atomically replaced,
the next unread JSON-RPC frame is handed to the new executable together with
the remaining stdio stream. The upgraded runtime—not the stale process—receives
that request. The old runtime never executes the handed-off frame; transport
failure remains an ordinary indeterminate outcome for callers to reconcile.
Sessions initialized on 11.18.5 advertise MCP tool-list change support; the
replacement emits notifications/tools/list_changed only after the logical
session has completed initialization, so conforming clients refresh cached
definitions as well as runtime behavior.
The unified coordination response identifies its live contract. Every
sage_inbox result now carries coordination_schema: "sage.inbox.v2", the
running mcp_runtime_version, and sender_replies_embedded: true|false. Monitors can
therefore reject or report a stale pointer-only session instead of silently
assuming that an empty addressed inbox also means no threaded reply arrived.
The existing bounded reply_items, inclusive watermark, composite catch-up
cursor, and passive sender-only authorization remain unchanged.
The upgrade from a pre-11.18.5 MCP process still requires one agent-session restart because that already-running older process cannot contain this handoff logic. Once a session starts on 11.18.5 or later, subsequent binary replacements use the automatic request-preserving handoff. Clients that ignore the negotiated tool-list notification must still re-list tools or reconnect to discover new definitions.
The consensus ceiling remains app-v26; v11.18.5 introduces no app-v27.
Container: ghcr.io/l33tdawg/sage:11.18.5. SDK 11.18.5.
What's New in v11.18.4
One inbox poll now surfaces both new work and threaded answers.
sage_inbox returns replies to messages you sent under the separate passive
reply_items key by default, while genuine inbound work remains under items.
Reply rows never inflate work counts and explicitly require no reply. Inclusive
reply_since polling prevents same-millisecond loss; truncated pages fail safe
with an exact composite-cursor catch-up action and forbid advancing the
watermark until the window is drained.
Release builders now enforce the patched Go floor. Root and natter
modules require Go 1.25.12, CI and release jobs resolve that exact go.mod
toolchain, every Go container builder uses 1.25.12, and pinned
govulncheck v1.6.0 scans both modules before either CI fan-in or release
publication can pass.
Legacy pipeline retention compares time chronologically and conservatively. SQLite purge eligibility no longer relies on variable-width RFC3339 text. Cutoffs are floored to SQLite's millisecond precision, so ambiguous same-millisecond rows are retained rather than deleted early; malformed read evidence also retains fail safe.
The consensus ceiling remains app-v26; v11.18.4 introduces no app-v27.
Container: ghcr.io/l33tdawg/sage:11.18.4. SDK 11.18.4.
What's New in v11.18.3
Same-key consensus submissions now fail closed across every producer in the running daemon. The dashboard, REST API, federation manager, voter, and upgrade watchdog share a per-key nonce lease. Once exact transaction bytes reach CometBFT, any unproven transport, status, RPC, decode, shape, hash, or height outcome fences that signing key until reconciliation proves those same bytes committed or permanently refused. Strict shared Comet decoders require a single bounded JSON document, explicit nested verdicts, the exact transaction hash, and a positive committed height for success.
Update restart advice now follows live fence state. A completed download no longer leaves stale restart guidance behind: retained update status reads recompute whether restart is currently safe, and the dashboard renders the server-provided instructions. Coordinated restarts are refused when a fence is present. Crash, power-loss, cross-restart, and separate-process CLI exposure still require durable pre-broadcast intent and remain explicitly out of scope.
The consensus ceiling remains app-v26; v11.18.3 introduces no app-v27.
Container: ghcr.io/l33tdawg/sage:11.18.3. SDK 11.18.3.
What's New in v11.18.2
A reply to a message you sent is readable again, through an advertised MCP
tool. Previously a recipient could answer, the durable row flipped to
completed, and the answer was reachable only through the passive REST
projection GET /v1/pipe/results — which no MCP tool ever called. sage_inbox
shows work addressed to you, not answers to you, and sage_message_status is
sender-only but deliberately payload-free. So in MCP and bookend clients the
reply was invisible and work round-tripped. v11.18.2 adds sage_message_replies
as an explicit sender-side read (SAGE now advertises 32 MCP tools) plus a
payload-free pointer inside sage_inbox that reports how many replies are
retained without ever presenting them as new work.
The reply read is exact-sender-only, passive, and honest about provenance.
Authorization is the SQL predicate from_agent = ? against the caller's own
signed identity — not the wider callerCanViewPipe rule the workflow route
uses — and no parameter names another agent, so the tool cannot serve as a
message-existence oracle. Reading claims nothing, acknowledges nothing, and
re-queues nothing. Every body is labelled untrusted data and attributed to the
agent that actually wrote it rather than the agent you addressed.
GET /v1/pipe/results gains a payload-free ?count_only=1 probe and a
composite (completed_at, pipe_id) before= cursor, so replies sharing a
millisecond are never stranded behind the page boundary. A store backend
lacking the optional capability answers 501 instead of an empty page that
would read as "no replies".
Memory, agent, RBAC, federation, and consensus behavior are unchanged; app-v26 remains the binary ceiling and v11.18.2 introduces no app-v27.
Container: ghcr.io/l33tdawg/sage:11.18.2. SDK 11.18.2.
What's New in v11.18.1
MCP session guidance now uses the protocol surface intended for it. SAGE
runs its per-session boot standing during initialize and returns the adaptive
full, bookend, on-demand, pending-review, or unavailable guidance through
initialize.instructions. The first real tool result is therefore only that
tool's payload instead of being prefixed with a 1.5–2.9 KB auto-connect block.
Repeated or concurrent initialization in one transport session reuses the same
standing without duplicating signed registration or caller-scoped reads.
Clients that skip the MCP initialization handshake keep the one-time first-tool
fallback for compatibility.
Legacy-lineage recovery now represents real skip-ahead history truthfully.
When retained Comet history proves a version jump such as 1→7 or 8→11, the
app-v21 doctor emits a v2 transition claim at the real activation height and
records the skipped predecessors as virtual, subsumed coverage. It never
invents interleaved heights or writes synthetic upgrade:applied:* records.
Every validator independently replays the retained history and hashes before
an explicit vote, and the immutable audit is installed atomically only when
app-v22 activates. Existing valid v1 receipts on already-upgraded app-v22+
chains remain readable; new v1 repair proposals fail closed.
The lineage change is confined to the exceptional app-v21 → app-v22 recovery ceremony. Memory, agent, RBAC, and federation policy are unchanged; app-v26 remains the binary ceiling and v11.18.1 introduces no app-v27.
What's New in v11.18.0
A connected pair is now the federation group users expect it to be. Each side explicitly exports the ordinary local agents it places in that pair. Every active ordinary agent on the other SAGE may then live-read those exported agents' owned domain trees by default—no matching local group, receiving domain, or linked-reader grant is required. A receiving operator can narrow that default with exact agent/domain denials. Local-only group membership is never exported transitively, and adding another federated agent is an explicit new export. Read remains borrowed; Copy still requires a source offer plus the receiver's Save here subscription, while remote memory Write remains reserved and fails closed.
Federated authorization now stays true through disclosure. The signed Read
plan and single-use challenge bind the exact source-agent standing, clearance,
export, agreement, policy generation, and negotiated authorization model. The
source authorization lease is revalidated and held until the destination query
finishes, so a concurrent rename-safe identity change, restriction, ownership
change, pause, or revoke cannot leak a result. CEREBRUM and sage_federation
also report authenticated-read readiness honestly, and the Docker acceptance
lane proves default Read, explicit denial, non-transitive exports, bidirectional
Copy backfill/incremental sync, and restart recovery.
People can address agents without giving up canonical identity. Local and
federated message targets accept a unique display or immutable registered name;
the resolved request and wire proof still carry only the canonical agent ID and
chain. Ambiguous local/remote collisions fail with bounded immutable choices
instead of selecting the first label. Federated replies now return an immutable
reply_event_id, and the replier can query that exact event's delivery status
without pretending it is a new inbox message.
Access Controls is now one usable control surface. Dedicated Agents, Groups, and Federation tabs use compact searchable/sortable lists and focused detail drawers instead of mounting every permission matrix at once. Modern and legacy URL deep links preserve the selected tab and exact local or federated identity. Dialog/drawer focus ownership, Escape/Tab handling, ARIA labels, and narrow-screen behavior are covered by browser-contract tests.
JOIN and upgrade recovery are bounded and explicit. A JOIN session still
expires after 15 minutes, while each pasted/scanned code gets up to five minutes
of Direct/relay discovery as long as its pairing screen remains open. v11.18.0
is also the first concrete release containing stopped-node backup --full,
recoverable restore --from, upgrade preflight, and the app-v21 → app-v22
upgrade lineage status|doctor|verify workflow. A legacy-lineage repair is
create-only, chain/current-state bound, embedded in the exact immutable upgrade
proposal, never auto-voted, and requires every validator to verify and vote
explicitly; an unverified anchor requires a deliberate acknowledgement.
The federation/UI work is off-consensus. The narrow lineage ceremony repairs only an eligible chain still at app-v21 before its governed app-v22 transition. Existing app-v22 through app-v26 chains are not rewritten, app-v26 remains the binary ceiling, and v11.18.0 introduces no app-v27. Both SAGEs should run v11.18.0 for the complete signed federation tuple; older peers fail closed rather than silently downgrade it.
Container: ghcr.io/l33tdawg/sage:11.18.0. SDK 11.18.0.
What's New in v11.17.15
Blank home-domain approval now does what the form promises. When an operator approves a writable pending agent without typing a home domain, CEREBRUM derives a readable slug from that agent's committed name, adds a cryptographically random suffix, and includes the resulting unowned domain in the same dual-signed approval transaction. An explicitly entered domain still wins. The unpublished v11.17.14 workflow was canceled after this browser-found regression, so v11.17.15 is the first published release containing the changes below.
Bulk domain recovery now completes on idle personal chains. CEREBRUM keeps an explicitly confirmed multi-domain transfer alive across the existing 50-block governance cooldown, shows the current/required block while consensus advances, and stops on every non-cooldown failure. Confirmed batches belong to the CEREBRUM session rather than one screen, so operators may navigate away and enqueue another transfer behind the active governance job. If an idle CometBFT clock rejects the first app-v20 authorization as too far ahead, the server re-signs the exact request once against the newly committed chain time; the proof window and every consensus authorization check remain unchanged.
Companion inbox setup now matches the profile’s purpose. Choosing the Companion/voice-bridge preset enables connected-SAGE inbox messaging by default; the independent emergency block remains available afterward. If an existing agent is blocked, Federation now keeps the warning visible and provides a one-click path to that exact agent and inbox switch in Access Controls.
v11.17.15 also contains the v11.17.13 Agents directory and Linux packaging changes below; v11.17.13 and v11.17.14 were never published after their release runs were canceled.
Included from v11.17.13
New agents now appear where operators expect them. Agents waiting for first
approval are separated from activated local principals and shown in a
conditional review queue at the top of Agents, with the existing atomic
approve/reject controls. Access Controls remains focused on activated local
agents. Exact ordinary agents advertised by connected SAGEs now have a distinct
From federation directory, including whether read-only group permissions are
unset or already linked; permission setup opens the existing Linked readers
control focused on that exact agent_id@chain pair. Federation transport,
ceremony, and Root identities are never cast as ordinary agents.
Linux preview packaging survives transient helper outages. The native-shell gate preloads every Tauri AppImage helper through a three-attempt bounded retry, an atomic reusable cache, and an exact SHA-256 allowlist. Partial or corrupt entries are rejected, retries report the helper and attempt, and persistent or changed upstream artifacts fail with deterministic diagnostics instead of being silently trusted.
This patch also refreshes the pinned Go runtime dependencies and CodeQL action. It changes no consensus rule, AppHash input, transaction type, key encoding, fork target, or application version. Existing v11.17 chains upgrade in place.
Container: ghcr.io/l33tdawg/sage:11.17.15. SDK 11.17.15.
What's New in v11.17.12
Federation agent sharing now fails safely and explains the real policy. The agent picker checks the selected local agent's federated-inbox capability before changing any shared domains, so an inbox blocked by policy can no longer leave a partial domain share followed by a misleading refresh error. Access Controls now shows an explicit Allow messages from connected SAGEs switch and changes only the independent federation-deny bit; Companion agents keep their existing role, clearance, home domain, and other restrictions.
The Tasks board stays inside the viewport. Four- and two-column layouts now allow every track to shrink below its content's intrinsic width, so long Done or Dropped cards wrap inside their columns instead of creating a page-level horizontal scrollbar or clipping the final column.
This patch changes no consensus rule, AppHash input, transaction type, key encoding, fork target, or application version. Existing v11.17 chains upgrade in place without rewriting trust, domain grants, agent acceptance, memories, or history.
Container: ghcr.io/l33tdawg/sage:11.17.12. SDK 11.17.12.
What's New in v11.17.11
CPU-only embeddings are faster, bounded, and observable. Native Ollama and
OpenAI-compatible batches replace per-record request loops, concurrent identical
work is coalesced without retaining a cross-agent plaintext cache, imports embed
in bounded windows after authorization, and MCP clients let current SAGE nodes
authoritatively queue their own vectors. Provider, model, dimension, timeout,
managed-Ollama, and amid configuration now describe one coherent vector space.
A reproducible sage-embedding-bench command and CPU deployment guide cover
measurement and tuning.
Idle nodes can transfer domains again. Newly signed dashboard governance proofs use the fresher safe clock when the latest committed block is old, while the consensus proof window remains unchanged and future-skewed clocks still fail closed. Federation connection details also expose Save and Revoke controls both above and below long permission catalogs, avoiding a full-page scroll.
This patch changes no consensus rule, AppHash input, transaction type, key encoding, fork target, or application version. Existing v11.17 chains upgrade in place without rewriting trust, domain grants, agent acceptance, memories, or history.
Container: ghcr.io/l33tdawg/sage:11.17.11. SDK 11.17.11.
What's New in v11.17.10
Federation visibility is symmetric again. CEREBRUM's single authenticated peer-status probe now preserves the peer-scoped domain permission and agent contact projections that the remote SAGE returned. A reachable connection can no longer show an agent from the other SAGE while claiming that its domains were never reported, and the reverse side receives the same shared-agent view. Transport binding internals remain hidden from the dashboard response.
This patch changes no consensus rule, AppHash input, transaction type, key encoding, fork target, or application version. Existing v11.17 chains upgrade in place without rewriting trust, domain grants, agent acceptance, memories, or history.
Container: ghcr.io/l33tdawg/sage:11.17.10. SDK 11.17.10.
What's New in v11.17.9
CEREBRUM's agent and recovery surfaces now reflect the operator's model. Friendly renamed-agent labels are used consistently, the Access Controls agent rail is wider, and the Agents directory is searchable by name or ID and sortable by recent presence, recent committed memory, or name. The busy agent directory now appears before the low-traffic governance controls. Federation permissions use separate outgoing and incoming tabs, so a large local domain catalog no longer buries the peer's shared-back view below an endless matrix.
Domain transfer recovery is ownership-safe and retry-safe. The dashboard distinguishes immutable memory authorship from canonical domain ownership, excludes the actual current owner from transfer targets, and treats a replay of an already-committed transfer as success. Governance proof timestamps are bound to the latest committed CometBFT time, preventing false five-minute-ahead rejections on recovering or CPU-starved nodes.
Messages now behave like an inbox, not a short-lived pipe. Omitted/zero TTL keeps local and federated work durable until handled, v11.17.8 unread rows are extended during upgrade, and canonical inbox/outbox history is no longer swept by the legacy 24/48-hour pipeline retention jobs. Callers can still request an explicit 1–1440 minute expiry.
sage_turn now reports only message_inbox_unread and its count; it never
claims or injects message payloads. Agents call sage_messages_receive to read
the inbox and use status/history for replies and lifecycle evidence.
Container: ghcr.io/l33tdawg/sage:11.17.9. SDK 11.17.9.
What's New in v11.17.8
The v11.17 security backlog is cleared in code. Pion DTLS and STUN are
upgraded to their patched releases in both the SAGE and Natter modules. Recall
result slices no longer use caller-derived allocation hints, app-v23 migration
keys avoid length-arithmetic preallocation, and the CEREBRUM inline-script
contract recognizes HTML tag case without a fragile sanitizer-style regexp.
The roadmap, architecture, federation guide, onboarding guide, and Python SDK
docs were reconciled to the then-current canonical Messages API and 24-hour
default TTL (superseded by v11.17.9 durable-until-handled delivery),
deprecated hidden sage_pipe* aliases, app-v26 authority names, signed macOS
in-place updater, and the remaining physical acceptance boundaries.
Container: ghcr.io/l33tdawg/sage:11.17.8. SDK 11.17.8.
What's New in v11.17.7
Releases no longer pause for a manual two-Mac approval. Publication still requires the exact staged macOS applications and DMGs to pass writable-copy, launch, signature, Team ID, notarization, and stapling verification, then continues automatically through immutable package and GitHub publication.
Federation now recovers across LAN changes, internet relays, restarts, and
roaming addresses. Signed route snapshots retain the stable peer identity,
rank safe Direct and Secure relay candidates, republish after relay reservation
changes, and migrate v11.17.4 p2p_peers state without treating stale routes as
authorization. Unsafe DNS, loopback, link-local, unspecified, multicast, mixed
peer-ID, and wrong-protocol routes fail closed.
Federated agent discovery and Messages now work as one durable inbox. Exact
peer_chain lookup disambiguates same-named agents. A previously authenticated
exact address can be queued while its node is offline, remains caller- and
policy-bound across restart, and is revalidated before any payload leaves the
sender. Canonical status independently reports transport, exact-recipient read,
and workflow completion to the original sender. Legacy sage_pipe* tools stay
callable for compatibility but are no longer advertised to new MCP clients.
A reproducible Docker federation acceptance lane covers the real product path. It exercises same-LAN links, relay-only isolated networks, both-sided IP churn, relay outage and recovery, expired route snapshots, v11.17.4 migration, offline queueing, recipient inbox/read/reply, and final sender confirmation.
Container: ghcr.io/l33tdawg/sage:11.17.7. SDK 11.17.7.
What's New in v11.17.5
Federated agent sharing now sends the canonical permission wire shape.
Choosing a named local agent may add the domains that agent owns to the trusted
connection. That automatic path now serializes the same permissions array as
the normal domain editor, so the peer can expose the agent contact and the two
agents can use canonical Messages/Inbox over the existing direct-or-relay link.
Upgrade recovery accepts the first valid revision-zero snapshot. Legacy databases can legitimately publish their first preserved-record inventory at projection revision zero. CEREBRUM can now deprecate an exact selected subset of that inventory while still requiring the revision field, positive count, typed confirmation, current Root authority, and atomic queue validation.
Federation enrollment now carries one validated route bundle from JOIN to roaming operation. Direct and secure-relay candidates survive the ceremony, the dashboard reports the route that actually carried authenticated traffic, and stale host windows fail closed. Canonical agent messaging uses the exact linked-reader relationship plus independent receiver-local consent on the same direct-or-relay transport.
Canonical Messages are the public agent-to-agent workflow.
sage_message_send, sage_inbox, sage_message_reply,
sage_message_status, and sage_message_history cover idempotent send,
receive, reply, receipts, and restart-persistent history. Legacy sage_pipe*
MCP tools remain compatibility aliases but are explicitly deprecated. The
federated proof verifier accepts the sender-local idempotency field in the
exact signed request without exporting that replay token into the peer event.
New messages now default to the full supported 24-hour inbox lifetime, rather
than expiring after one hour while a recipient agent may be offline.
CEREBRUM recovery and consensus stay usable on upgraded nodes. The
consensus page authenticates its scope request, incompatible historical
domain-continuity candidates are retired instead of being reproposed every
block, and recovery deprecation records an honest recovery activity event.
The recovery authority controls use a responsive grid, so the explanatory
copy and selectors no longer collapse into a horizontally scrolling row.
Access Controls also normalizes historical empty groups to members: [], so a
valid empty group cannot throw during the first render and leave the page stuck
on “Loading consensus access policy…”.
Historical app-v25 home defects no longer prevent app-v26 repair from
starting. Nodes with the narrow legacy shared_home shape may rebuild their
local agent serving projection long enough for the existing deterministic
app-v26 migration to run. Eligibility and validation share one Badger snapshot,
completed app-v26 chains stay strict, and a concurrent repair falls back to one
strict retry. This changes no memory, historical author, ownership history, or
prior block outside the already-governed app-v26 repair.
Large federation agreements stay responsive. CEREBRUM renders bounded 75-domain windows, keeps existing grants and retained subscriptions first, and skips reconciliation when polling returns identical state. Search, bulk actions, and Save still operate on the complete filtered permission set and full draft rather than only the rendered rows.
Local MCP clients use the listener SAGE actually binds. Generated configs,
hooks, bundles, and internal defaults now use 127.0.0.1 instead of allowing
localhost to resolve to an unbound IPv6 ::1. sage_find_agent also
preserves its bounded federated continuation cursor when a fuzzy local result
exists, so a caller can explicitly request the next peer page without any
automatic federation walk.
App-v26 makes Access Group authority explicit and reviewable. Every local
group now stores one deterministic member authority: read, read_write, or
read_write_modify. Existing groups migrate to the safe read baseline at
the strict H+1 fork boundary. A domain owner always retains full control of its
own domain; group membership is additive, the strongest applicable group wins,
and removing an agent revokes only that cross-member relationship without
touching the agent's own domains. Linked federated agents remain read-only
guests and can never acquire local Write, Modify, ownership, or governance.
Local agent messaging now has one canonical, durable receipt contract. An
idempotent send, exact receive-batch replay, recipient-only reply/read
acknowledgement, and sender-only payload-free status projection use the existing
encrypted pipeline inbox rather than a second queue. Connected HTTP MCP SSE
sessions for the exact recipient may receive a metadata-only wake-up; this is a
best-effort hint, never presence, delivery, comprehension, or read evidence.
The enforced sage_turn reminder/checkpoint nags are removed.
CEREBRUM helps Root finish historical recovery instead of leaving a warning. Unresolved preserved records can be inspected through bounded safe previews, selected, assigned to an active local ordinary agent when exact verified evidence permits it, or deprecated. Already-deprecated rows are excluded. Authorship, content, domains, and chain history remain immutable; assignment changes only current operational ownership. Conflicting or unverifiable rows remain deprecate-only.
Linked SAGE discovery closes over the relationship agents can actually use. Caller-scoped directory results include only consented linked peers and expose their exact address plus registered/display name metadata. The same authority is enforced for direct and secure-relay paths; discovery grants no remote memory write or local group membership.
Operator mutations and signed updates fail safely without lying. CEREBRUM reconciles uncertain consensus responses against canonical state and repairs the local agent projection after a committed approval. Access Controls can also commit a new agent display label without changing its immutable registered name, agent ID, boot purpose, domains, or authorship; the rare Root handover card now sits below everyday agent and group controls. The macOS release gate mounts the signed DMG, copies the app to a fresh writable APFS location, verifies the exact leaf identities and version before and after first execution, and publishes only that verified immutable asset. CEREBRUM now stages that signed DMG, verifies the replacement, swaps the installed application through a separate helper, and restarts into the new build with bounded readiness checks and rollback. Manual drag-and-drop remains the explicit fallback. Linux keeps its verified in-place updater.
This is a governed consensus upgrade from app-v25 to app-v26. Existing chains advance in place; memories, historical authors, domains, and prior blocks are not rewritten.
Container: ghcr.io/l33tdawg/sage:11.17.5. SDK 11.17.5.
What's New in v11.16.4
Existing nodes recover from stale app-v23 serving projections at startup. A rebuildable local SQLite projection whose old duplicate policy fields disagree with the canonical committed enrollment is normalized from that canonical policy record instead of preventing the node from starting. This is a local read-model repair only: it does not alter blocks, memory content, historical authors, domains, access groups, or the consensus application version.
The release pipeline verifies the installer that users actually download.
After macOS packages upload, CI downloads the staged DMG, checks its checksum,
mounts it, and verifies the app signature, Gatekeeper assessment, and
notarization before publication. The MCP server also no longer spends an
agent's context budget on repeated per-tool sage_turn reminder messages.
Claiming a message no longer makes it disappear for either participant. The active inbox remains a pending-only, claim-on-read work queue so old work does not reappear in every turn. A new passive retained inbox/outbox history lets the recipient reopen claimed or completed work and lets the sender revisit its local lifecycle until the normal transient pipeline retention sweep. Agents can also list the signed active local directory—with display name, immutable registered name, provider, and exact agent ID—before addressing a message, instead of guessing a recipient from a fuzzy provider label.
CEREBRUM now settles operator actions against the canonical chain instead of undoing them in the browser. Clearing a terminal task column keeps cards out of intermediate refreshes while the local projection catches up, then reloads the authoritative board. A lost or late commit response is reported as confirmation in progress rather than the false claim that nothing changed; only a definite consensus rejection is red. A multi-manager deprecation that opens a challenge is shown honestly as awaiting its distinct eligible confirmation rather than called cleared.
Access Groups and agent recovery are usable in the flow operators actually use. Dragging one active local agent onto another creates or extends the narrowest local group, so members read each other's owned domains by default until the operator explicitly selects Read + write or Read + write + modify for that group. Global Manager labels never silently widen the selected group permission. Dragging a member back out revokes only that group relationship. CEREBRUM also settles agent removal and first-use domain authority against committed state, rather than leaving a stale progress screen or asking a newly-created domain to retry its first operation.
Federation no longer requires a relay reservation to use a working direct route. A trusted pair may connect immediately over its authenticated direct candidate—especially useful on the same LAN—and keeps the secure relay as an automatic roaming/NAT fallback. Direct-only route bundles now validate on both the dashboard and peer transport paths.
This patch does not rewrite memories, domains, historical authors, existing groups, or chain history. It keeps consensus application version 25 and the existing governed upgrade path unchanged. Existing nodes upgrade in place.
Container: ghcr.io/l33tdawg/sage:11.16.4. SDK 11.16.4.
What's New in v11.16.2
App-v25 repairs historical continuity without rewriting history. It is the strict H+1 successor to app-v24. New submissions receive an immutable canonical envelope: a memory ID can be replayed exactly, but cannot later be reused for different content, author, domain, or classification. That closes the old projection-overwrite path that could leave an agent able to write a domain but unable to read it back.
On upgrade, SAGE scans historical SQL rows against canonical state in the background. Complete, content-hash-verified records are adopted through bounded Root-authorized, validator-attested governance batches. No memory content, author attribution, domain, classification, or earlier block is rewritten. For each recovered local domain, the earliest verified historical writer is retained as the operational owner; every other verified local writer is restored into the exact local Access Group with read/write continuity. If the earliest writer is no longer a valid local principal, CEREBRUM Root owns the recovered domain rather than promoting a later writer by guesswork.
One bad historical row can no longer blank CEREBRUM or take agents offline.
v11.16.2 quarantines each unverified record individually. Broad list/search,
graph, timeline, stats, and dashboard-health reads continue with the verified
set and disclose a partial-projection state. A completed audit returns
/ready as HTTP 200 / degraded; actual backend failures and incomplete
audits remain unavailable. This keeps supervisors, MCP bootstrap,
sage_inception, and healthy agent work online without pretending incomplete
data is safe.
Unreadable or conflicting records are preserved byte-for-byte. CEREBRUM Root can retry the evidence scan or explicitly deprecate the exact unresolved inventory after a typed confirmation; deprecation retires it from automatic repair and normal views but does not delete historical data. See App-v25 upgrade and recovery.
Container: ghcr.io/l33tdawg/sage:11.16.2. SDK 11.16.2.
What's New in v11.16.0
App-v24 closes the canonical terminal-hash lifecycle defect without rewriting
history. New memory submissions bind content_hash to the exact SHA-256 of
their content, and challenge, deprecate, and other terminal transitions preserve
that canonical hash. App-v24 activates at the strict height after its app-v23
predecessor, so the activation block and every earlier block retain their exact
historical semantics. A governed, Root-planned validator vote can re-anchor
eligible historical terminal rows in bounded, atomic, idempotent batches from
their unchanged canonical content. The repair changes neither content,
authorship, domain ownership, nor prior blocks.
Fresh first-party Mynah nodes now wait for the safe protocol floor instead of
starting mute or writing through the vulnerable interval. Direct app-v23
genesis remains the authenticated bootstrap origin, but /ready reports
waiting_for_app_v24 until the next admitted transaction will execute under
app-v24. Consensus independently rejects direct-genesis Companion memory and
co-commit writes during that short governed climb, so bypassing the readiness
endpoint cannot reproduce the defect. Personal nodes require app-v24 even when
optional future auto-upgrades are disabled. This nar
Related MCP servers

Banyan Memory
Persistent, governed local memory for MCP-compatible AI clients.

AIOps Field Notes
Audit an MCP config, price a model, size a GPU, explain network config drift. Key-free.
whatismynetip
Subnet math, port and MAC lookups, DNS, DNSBL, TLS cert inspection, public IP. No account.
NetOps Field Notes
Config drift, CIS/PCI checks, 802.1X diagnosis, certs inside configs, topology, change pre-flight.
SecOps Field Notes
CVSS scoring, IOC extraction, email header triage, hash/JWT/timestamp decoding, CISA KEV lookup.

io.github.labarilem/brainfaq-mcp
MCP server for the BrainFuck programming language