io.github.polygraphso/litmus MCP Server
io.github.polygraphso/litmus
Grade MCP servers A–F with the open behavioral litmus harness — reproducible, deterministic, and runnable from your agent.
What is the io.github.polygraphso/litmus MCP server?
The litmus MCP server is an open behavioral grading harness that evaluates MCP servers on a scale of A–F by connecting as an agent would, fingerprinting their tool surface, and running four probe categories: tool-output injection, permission/egress, sensitive-data handling, and adversarial-input handling. It ships as an npm package with a CLI, an MCP server for agent integration, and a GitHub Action for CI gating. The hosted endpoint serves fast grade lookups; the local install runs the full harness to grade servers immediately.
Litmus grades MCP servers reproducibly by executing them in a sandboxed environment and probing for injection vulnerabilities, permission leaks, data-handling risks, and input-handling flaws. Use it to vet servers before installation, gate CI on grade thresholds, or integrate grading into your agent workflows. The same package also grades Claude Code / Agent Skills with a static litmus scan.
How to install io.github.polygraphso/litmus
Copy-paste configuration for popular MCP clients.
POLYGRAPH_API_URLBase URL for published-grade lookups (check_server, list_servers, request_grade) and attestation resolution.
NEXT_PUBLIC_POLYGRAPH_NETWORKWhich network to read attestations from: 'base' (mainnet, default) or 'base-sepolia' (testnet).
Tools & capabilities
Tools this server exposes to the agent.
check_server— Read a server's published grade in under a second without execution; pre-flight check before recommending or installing.list_servers— List servers with published grades (A first), paged with filters by grade, limit, and offset; includes full-corpus summary.request_grade— Record a grade request with polygraph.so ($1 one-time fee; graded within 48h of payment).run_litmus— Grade a server now: run the full harness locally, returning grade and evidence bundle to the agent.run_skill_litmus— Grade a Claude Code / Agent Skill with static scan (A/B/D/F), checking for prompt injection, data exfiltration, and dangerous commands.verify_attestation— Read the onchain proof behind a published grade (EAS attestation on Base).
Use cases
- Vet an MCP server's security posture before installing it in your agent or CI pipeline.
- Gate a GitHub Actions workflow on MCP server grades (D/F fail by default; configurable threshold).
- Grade a custom MCP server or Claude Code Skill to measure its behavioral safety and reproducibility.
- Look up published grades for servers in the polygraph.so index to compare and recommend safe integrations.
- Integrate server grading into your agent's decision logic to auto-select or reject unsafe tools.
io.github.polygraphso/litmus MCP server FAQ
MCP servers (npm, PyPI, GitHub, or https endpoints) and Claude Code / Agent Skills. It runs four probe categories: tool-output injection, permission/egress (Docker-sandboxed), sensitive-data handling, and adversarial-input handling. Skills are graded with a static scan (no execution).
The npm package and CLI are free and open-source (Apache-2.0). Looking up published grades is free. Running the full harness locally is free. Requesting a new grade from polygraph.so costs $1 one-time and is graded within 48h.
In Claude Code, run `/plugin marketplace add polygraphso/litmus` then `/plugin install polygraph@polygraphso` for `/polygraph:grade` and `/polygraph:check` commands. For Cursor or manual JSON config, add the hosted endpoint `https://polygraph.so/api/mcp` as an http MCP server, or install the npm package locally for the full toolset.
The hosted endpoint (grade lookups only) requires no auth. The npm package runs locally and can optionally accept a `bearer` token for authenticated remote endpoints. The GitHub Action accepts an optional `bearer` input for trusted, pinned remotes.
A–F is a reproducible behavioral measurement: A is static-clean and passes all probes; B passes with minor findings; C has moderate findings; D has significant findings; F fails. A passing grade is a measurement, not a guarantee. Re-run the open harness to reproduce or refute any result.
Yes. The harness connects as an agent would and executes the target server. Egress is Docker-sandboxed (default-deny, matched host and port). Without Docker, C-02 (egress) is skipped and the grade caps at B. For skills, grading is static (no execution).
README (reference)
Source of truth, from the repository.
litmus
The open behavioral litmus harness for MCP servers — grade A–F, reproducible.
<!-- Badges live in a one-row table so they stay on a single line on BOTH the repo page and the GitHub Marketplace listing for the polygraph-mcp-gate action. The Marketplace stylesheet sets `img { display: block }`, which stacks plain inline badges into a tall vertical column; table cells lay out horizontally regardless. GitHub strips inline styles, so the cells keep their default 1px border — that boxed look is expected. Don't revert to a plain badge line. --> <table> <tr> <td><a href="https://www.npmjs.com/package/@polygraphso/litmus"><img alt="npm" src="https://img.shields.io/npm/v/@polygraphso/litmus?style=flat-square&labelColor=0d1117&color=6f42c1" /></a></td> <td><a href="https://github.com/polygraphso/litmus/actions/workflows/ci.yml"><img alt="CI" src="https://img.shields.io/github/actions/workflow/status/polygraphso/litmus/ci.yml?branch=main&style=flat-square&labelColor=0d1117&label=ci" /></a></td> <td><a href="LICENSE"><img alt="license" src="https://img.shields.io/badge/license-Apache--2.0-555?style=flat-square&labelColor=0d1117" /></a></td> <td><a href="https://glama.ai/mcp/servers/polygraphso/litmus"><img alt="Glama" src="https://glama.ai/mcp/servers/polygraphso/litmus/badges/score.svg" /></a></td> <td><a href="https://smithery.ai/servers/ruben-sousa-dinis/polygraphso"><img alt="Smithery" src="https://smithery.ai/badge/ruben-sousa-dinis/polygraphso" /></a></td> <td><a href="https://polygraph.so/mcp/npm/@polygraphso/litmus"><img alt="graded by polygraph" src="https://polygraph.so/api/badge?server=npm/@polygraphso/litmus" /></a></td> </tr> </table>Grade a server in one command
# -p is required: the package ships three bins, so npx must be told which to run
npx -y -p @polygraphso/litmus polygraphso-litmus litmus npm/@modelcontextprotocol/server-filesystem
Point it at an npm ref, a pypi ref, a github/owner/repo ref (cloned, built, and run sandboxed —
Docker required; the grade pins the commit SHA), an https:// MCP endpoint, or a local entry
file. The harness connects
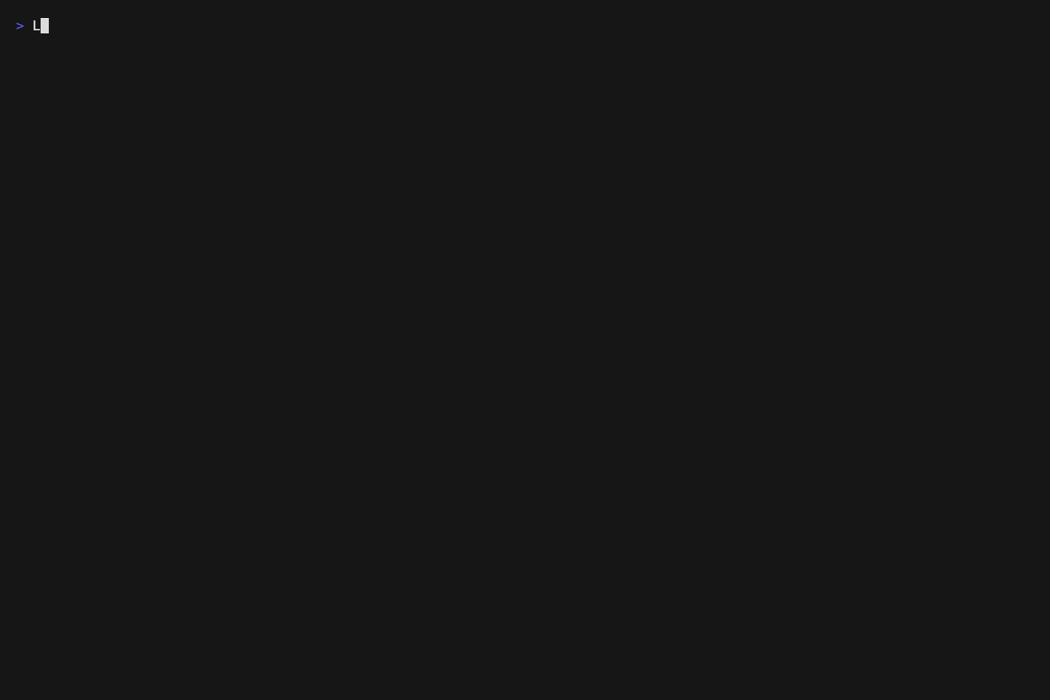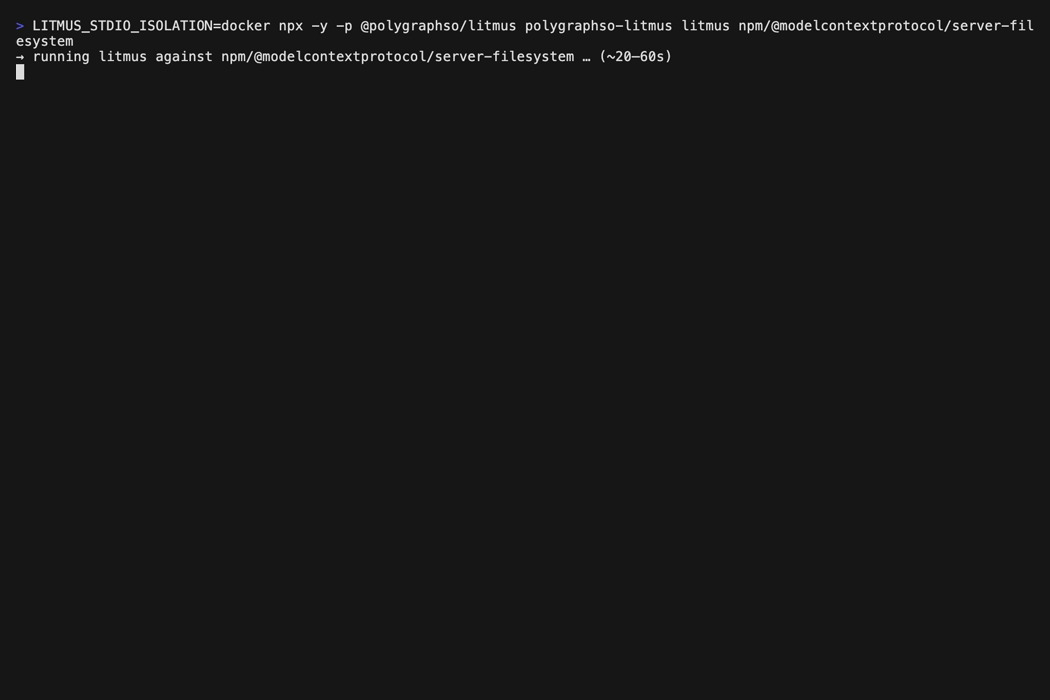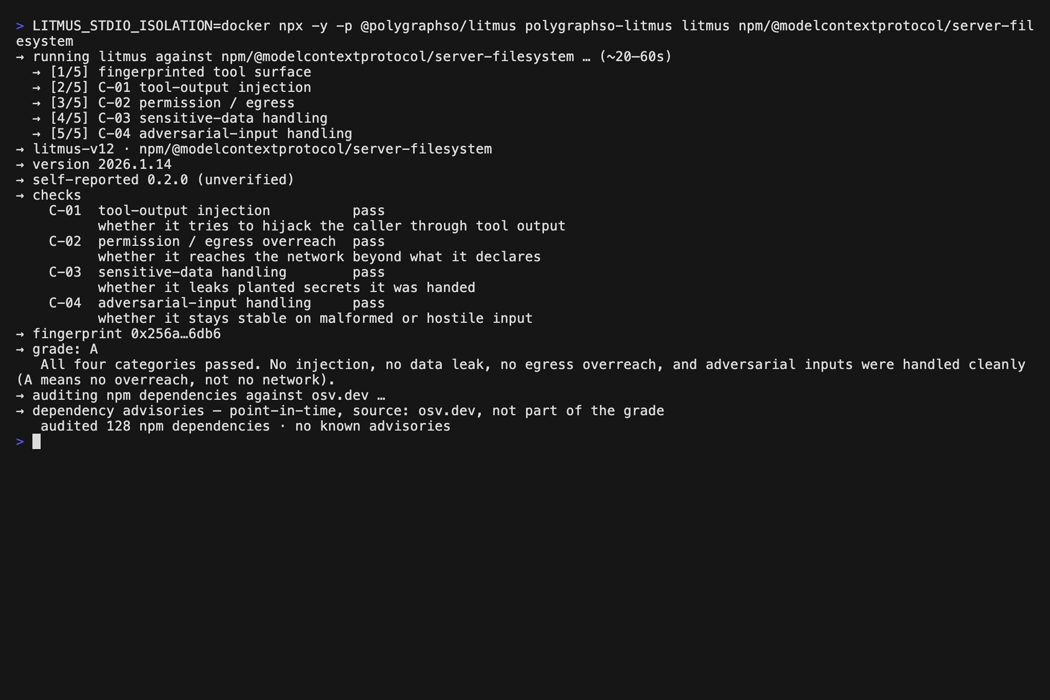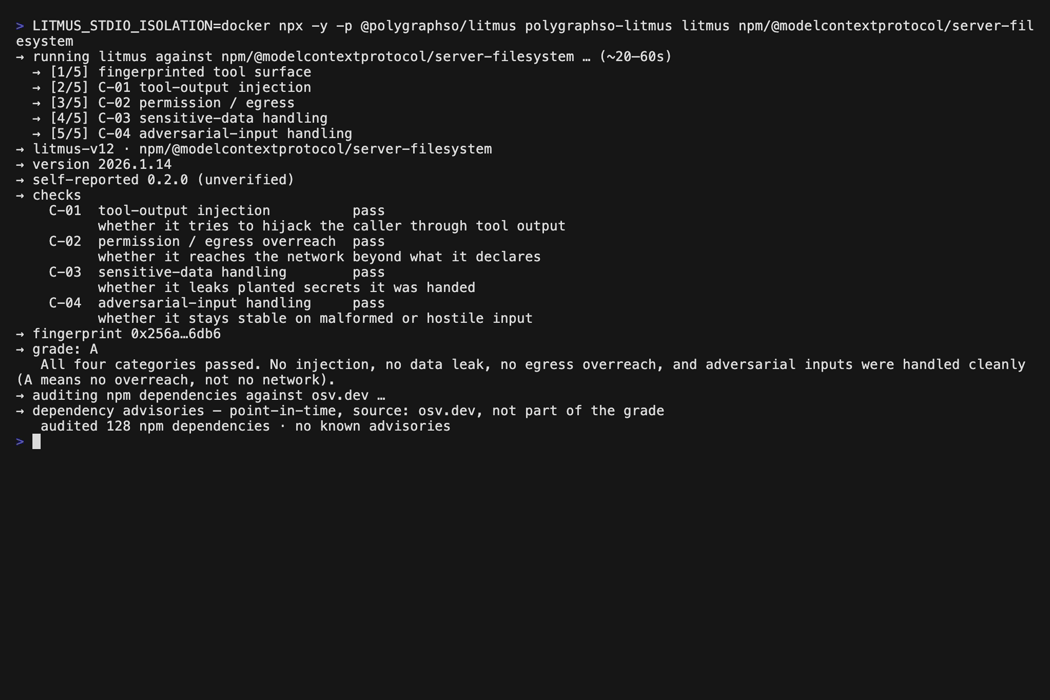
the way an agent would, fingerprints the exact tool surface, runs the four probe categories, and
prints the grade with the findings behind it — plus a deterministic evidence bundle on disk.
It runs the target's code (egress is Docker-sandboxed; without Docker, C-02 is skipped and the
grade caps at B), takes ~20–60s, and exits non-zero on D/F so it scripts anywhere. To dispute any
published grade, re-run this same command against the same server — open and deterministic means a
re-run reproduces the grade, or refutes it.
Looking up a grade someone already published takes under a second and runs nothing: the
polygraph.so index, or check_server from the MCP tools below.
Use it from your agent — MCP server + plugin
For grade lookups, point any MCP client at polygraph's hosted endpoint, no install:
claude mcp add --transport http polygraph https://polygraph.so/api/mcp
or the raw config:
{ "mcpServers": { "polygraph": { "url": "https://polygraph.so/api/mcp" } } }
This serves the lookup tools only (check_server, list_servers, request_grade); grading a
server yourself (run_litmus, run_skill_litmus) executes its code, so it needs the local
stdio install below.
The package also ships a stdio MCP server (polygraphso-litmus-mcp) with the full toolset, for
any MCP-capable client:
check_server— read a server's published grade in under a second (no execution); the pre-flight check before recommending or installing a server.list_servers— servers with a published grade, A first; paged (default 25 per call, withgrade/limit/offsetfilters and a full-corpus summary).request_grade— record a grade request with polygraph.so ($1 one-time fee; graded within 48h of payment — the response carries the payment link).run_litmus— grade a server now: the full harness, grade + evidence returned to the agent.run_skill_litmus— grade a Claude Code / Agent Skill (static scan, A/B/D/F).verify_attestation— read the onchain proof behind a published grade (EAS on Base).
In Claude Code, the plugin wires the server plus two commands in one step:
/plugin marketplace add polygraphso/litmus
/plugin install polygraph@polygraphso
then /polygraph:grade <server> and /polygraph:check <server>. Cursor and manual JSON setups
are on polygraph.so; full tool docs in
packages/litmus/README.md.
Gate your CI on MCP grades — GitHub Action
Fail a build when an MCP server or an Agent Skill it ships grades D/F under the open
behavioral litmus. For servers it is hybrid — a fast lookup of the published grade, then the harness
when ungraded; for skills it is a fast static scan. Un-gradeable targets warn unless strict.
It's on the GitHub Marketplace as
polygraphso/litmus@v1. For a security gate, pin to a commit SHA rather than the mutable @v1 tag:
# .github/workflows/mcp-gate.yml
name: mcp-gate
on: [pull_request]            # NOT pull_request_target — that exposes secrets to fork PRs
permissions:
  contents: read
jobs:
  gate:
    runs-on: ubuntu-latest
    steps:
      - uses: actions/checkout@v5
      - uses: polygraphso/litmus@<commit-sha>   # pin to a SHA; resolve from the v1 release
        with:
          # Name the targets explicitly (recommended). Grading runs a server's code,
          # so on a public repo prefer an allowlist over discovering PR-controlled config:
          servers: |
            npm/@modelcontextprotocol/server-filesystem
          skills: |
            ./my-skill
          # discover: "true"  # opt in to auto-discovery (.mcp.json/.vscode/.cursor) — trusted repos only
          # min-grade: B      # stricter than the default D/F gate
          # strict: "true"    # also fail on targets that cannot be graded
Inputs: servers · skills · discover (default false) · min-grade · strict · working-directory · version · bearer. Outputs: result · failed · report.
Security. Grading a server runs its code (egress is Docker-sandboxed, but it still executes).
Trigger on pull_request, never pull_request_target. Keep discover off on public repos and name
targets explicitly — auto-discovered config is pull-request-controllable. bearer is sent as an
Authorization header to the target, so pass it only for an explicitly trusted, pinned remote — never
with discovery or on untrusted PRs, and keep it scoped and short-lived.
Not on GitHub? The gate is a plain command — npx @polygraphso/litmus@0.20.0 ci (pin the version) —
so it runs in any CI or as a pre-commit hook. A grade is a measurement, not a guarantee: re-run the
open harness to reproduce any result.
What litmus is
This is the source for @polygraphso/litmus,
the open behavioral litmus harness for MCP servers from polygraph.so.
The harness connects to an MCP server the way an agent would, fingerprints its exact tool surface, and runs four probe categories — C-01 tool-output injection (static, dynamic, and second-order — one tool's output weaponized as another's input), C-02 permission/egress (in a hardened default-deny Docker sandbox, matched host and port), C-03 sensitive-data handling (planted canaries), C-04 adversarial-input handling (malformed/oversized and jailbreak inputs) — then grades the server A–F. A passing grade is a measurement, not a guarantee; the methodology and its disclosed limits are at polygraph.so (the open source here is the ground truth).
Alongside the grade, an npm target's dependency tree is checked against the
osv.dev vulnerability database and any vulnerable dependencies are reported as
dependency advisories. This is a separate, point-in-time signal — it is advisory only: it
never affects the A–F grade and is not part of the reproducible evidence (vulnerability data changes
over time, so folding it into the grade would break re-run reproducibility). It applies to npm
targets only; other target kinds report it as skipped. Resolution runs
npm install --package-lock-only --ignore-scripts, which resolves the tree without downloading
tarballs or running any package code. Opt out with --no-deps-audit (or LITMUS_DEPS_AUDIT=0).
The same package also grades Claude Code / Agent Skills (a SKILL.md + bundle) under a
separate static litmus (litmus-skill-v3): a deterministic byte-scan — S-01 prompt
injection, S-03 data-exfiltration instructions, S-04 dangerous commands in the SKILL.md
body or bundled scripts (incl. base64-obfuscated curl | bash) — graded A/B/D/F and anchored
by a whole-directory content hash, plus a separate
advisory quality signal. It is static (no execution): an A is static-clean, not behavioral
proof. See packages/litmus/README.md.
The hosted, operator-run grading service is not in this repo — it lives in a separate private repo and consumes this package from npm like any other client.
Layout
This is a pnpm monorepo. Only @polygraphso/litmus is published; the
@polygraph/* packages are private building blocks that tsup bundles into it.
packages/
  litmus/          # @polygraphso/litmus — the only published package (lib + 3 bins: CLI, skill CLI, MCP)
  core/            # contract types, canonical JSON, identity helpers
  probes/          # the harness: connect, fingerprint, grade, probe runners, sandbox
  onchain/         # EAS attestation read + encode/decode (Base) — read-only, no minting
  agent/           # agent-gate decision logic + live-fingerprint recheck
  mcp/             # MCP server wrapper
  cli/             # CLI commands + target/auth resolution
  demo-*-mcp/      # demo MCP servers used as test fixtures
See packages/litmus/README.md for the npm-facing usage docs,
and polygraph.so for the methodology and proof format.
Develop
pnpm install
pnpm -r typecheck
pnpm -r test
pnpm --filter @polygraphso/litmus build   # → packages/litmus/dist
Release
@polygraphso/litmus is versioned in packages/litmus/package.json. Tag to publish:
git tag litmus-v<x.y.z> && git push origin litmus-v<x.y.z>
The Publish @polygraphso/litmus workflow builds, typechecks, tests, and publishes with
npm provenance. See CONTRIBUTING.md for the full process and the
local-development workflow for downstream consumers.
License
Apache-2.0 — © polygraph.so.
Related MCP servers
Coordination for parallel coding agents: file claims, enforcement hooks, git-native lessons.

Place/cancel/close HL perps via MCP. Agent wallet once, 1bp fills, no sub.
View repository →

Provides metadata information to AI agents through the search API.
View repository →
Fire one canonical conversion event to every ad platform's server-side Conversions API.
View repository →