io.github.sinewaveai/agent-security-scanner-mcp MCP Server
io.github.sinewaveai/agent-security-scanner-mcp
Security scanner for AI agents: blocks prompt injection, detects fake packages, audits MCP servers, and scans code vulnerabilities.
What is the io.github.sinewaveai/agent-security-scanner-mcp MCP server?
The agent-security-scanner-mcp is a security layer for AI coding agents that scans code, MCP servers, prompts, and dependencies for vulnerabilities and AI-specific risks. It provides A-F security grades and catches prompt injection, package hallucination, MCP tool poisoning, and vulnerable generated code before agents execute them.
This scanner protects AI agents like Claude Code, Cursor, and Windsurf by detecting security risks in agent-generated code, MCP servers, prompts, and dependencies. Run it before trusting new code, tools, or packages to catch SQL injection, XSS, command injection, hallucinated packages, prompt injection, and MCP tool attacks. Works as a CLI tool, MCP server, or GitHub Action.
How to install io.github.sinewaveai/agent-security-scanner-mcp
Copy-paste configuration for popular MCP clients.
Tools & capabilities
Tools this server exposes to the agent.
scan_project— Full project scan with A-F security gradescan_security— Single-file security scanscan_diff— Scan changed files only between branchesscan_mcp_server— Audit an MCP server before installationscan_agent_prompt— Detect prompt injection and jailbreak attemptsscan_agent_action— Pre-execution safety check for shell/file/network actionscheck_package— Verify a package exists and is not hallucinatedscan_packages— Verify imports/dependencies in a filesbom_generate— Generate CycloneDX software bill of materialssbom_scan_vulnerabilities— Scan dependencies for CVEs using OSV.devcr_agent— LLM-powered semantic code review using project intent
Use cases
- Scan AI-generated pull requests for vulnerabilities before merging
- Audit MCP servers for tool poisoning, spoofed names, and command execution risks
- Detect hallucinated package names that attackers could squat on
- Check code diffs for SQL injection, XSS, command injection, and unsafe crypto
- Generate SBOMs and scan dependencies for known vulnerabilities before release
- Verify AI-suggested dependencies exist in npm, PyPI, RubyGems, and other ecosystems
io.github.sinewaveai/agent-security-scanner-mcp MCP server FAQ
A security scanner that protects AI coding agents by detecting vulnerabilities, prompt injection, MCP tool attacks, and hallucinated packages in agent-generated code, prompts, and dependencies.
Yes, it is MIT licensed and available as an npm package. The CLI and MCP scans are local; semantic review (cr-agent) uses your chosen LLM provider.
Run `npx agent-security-scanner-mcp init cursor` or `npx agent-security-scanner-mcp init claude-code`, then restart the client. The scanner becomes available as an MCP tool.
Rule-based CLI and MCP scans are entirely local. Only the optional cr-agent semantic review uses an external LLM provider you choose.
Vulnerable code patterns (SQL injection, XSS, command injection, unsafe crypto), MCP tool poisoning, prompt injection, hallucinated packages, unsafe agent actions, and dependency vulnerabilities.
Run `npx agent-security-scanner-mcp scan-diff --base main --target HEAD --verbosity compact` and `npx agent-security-scanner-mcp scan-packages ./src/app.ts npm --verbosity compact`.
README (reference)
Source of truth, from the repository.
agent-security-scanner-mcp
Security scanner for AI coding agents, MCP servers, prompts, and AI-suggested packages.
Run it before Claude Code, Cursor, Windsurf, Cline, OpenCode, or another agent trusts new code, tools, prompts, or dependencies.


Copy-Paste Start
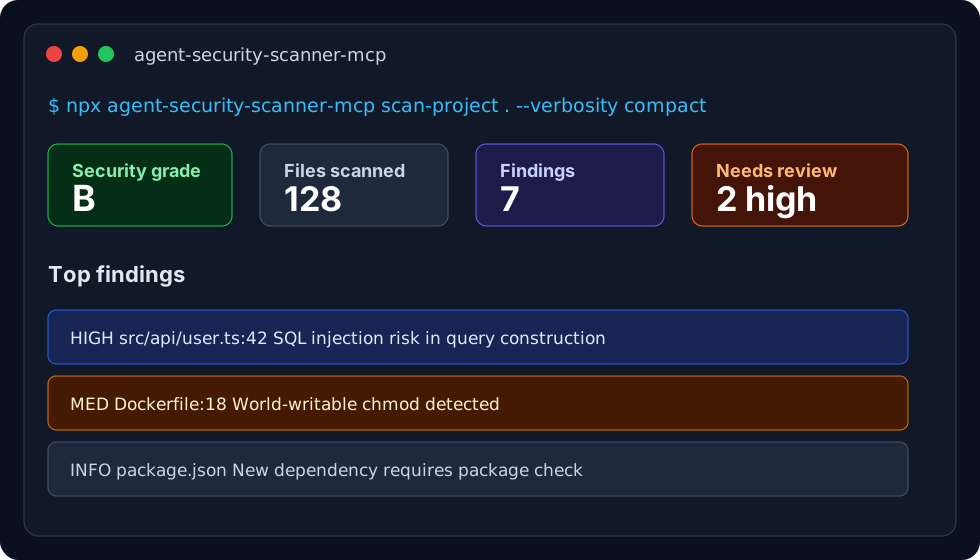
Scan any repo and get an A-F agent security grade:
npx agent-security-scanner-mcp scan-project . --verbosity compact
Install the scanner into your AI coding client:
npx agent-security-scanner-mcp init claude-code
Replace claude-code with cursor, claude-desktop, windsurf, cline, kilo-code, opencode, or cody.
Audit an MCP server before adding it to an agent:
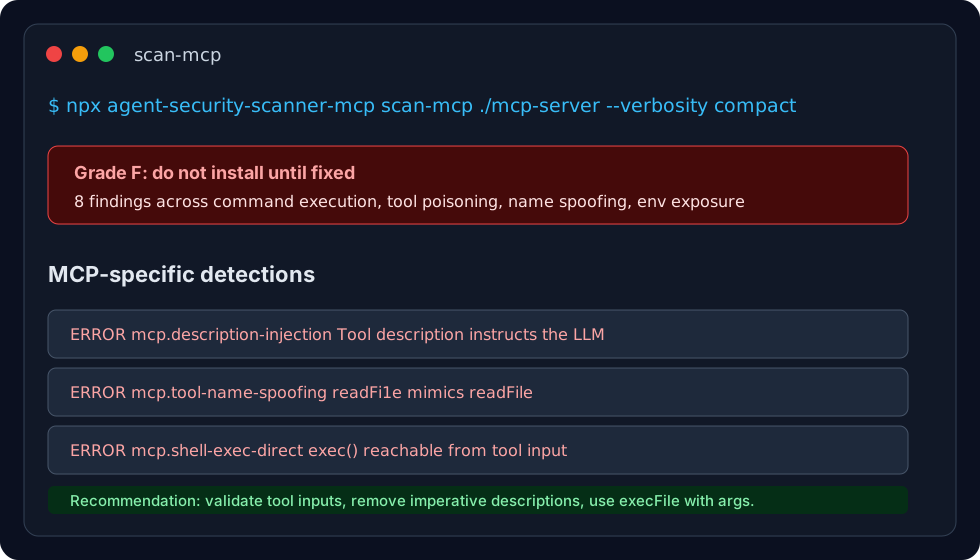
npx agent-security-scanner-mcp scan-mcp ./path/to/mcp-server --verbosity compact
Check AI-generated imports for package hallucinations:
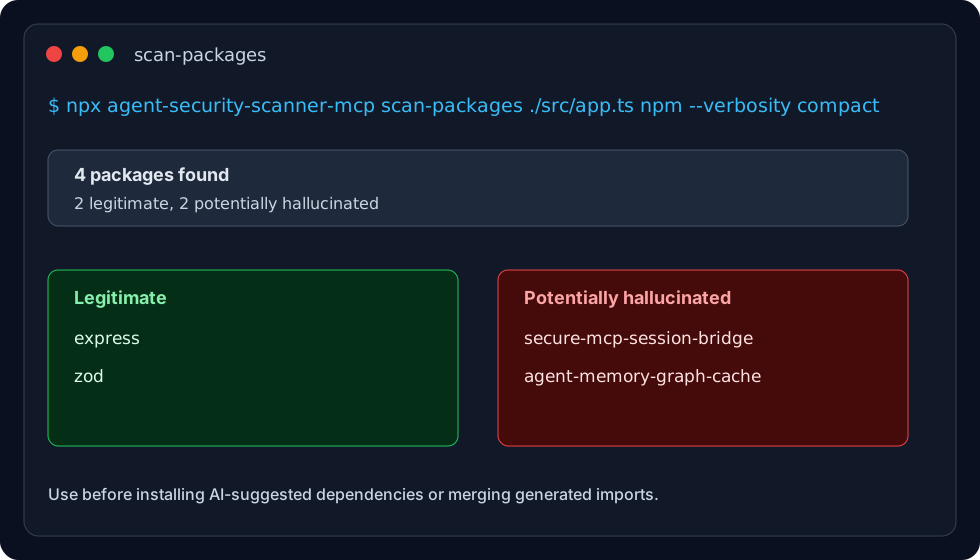
npx agent-security-scanner-mcp scan-packages ./src/app.ts npm --verbosity compact
What It Catches
| Risk | Why agents need it | Command |
|---|---|---|
| Vulnerable generated code | Agents can introduce SQL injection, XSS, command injection, unsafe crypto, and secrets | scan-project, scan-security, scan-diff |
| MCP server attacks | MCP tools can poison descriptions, spoof names, exfiltrate env vars, or execute commands | scan-mcp |
| Prompt injection | Agents often process untrusted docs, tickets, pages, and tool output | scan-prompt |
| Unsafe agent actions | Catch dangerous shell/file/network actions before execution | scan-action |
| Hallucinated packages | AI often invents dependency names that attackers can later squat | check-package, scan-packages |
| SBOM and CVEs | Generate CycloneDX SBOMs and scan dependencies with OSV.dev | sbom-generate, sbom-vulnerabilities |
| Semantic review | LLM-powered review that uses project intent to find context-aware issues | cr-agent |
Screenshots
Project Scan
MCP Server Audit
Package Hallucination Detection
Demos
Run a safe local demo that creates intentionally vulnerable fixtures, scans them, and cleans them up.
# MCP audit demo: tool poisoning, spoofed tool name, command execution, secret exposure
npx agent-security-scanner-mcp demo --type mcp --no-prompt

# Package hallucination demo: real imports mixed with fake AI-generated package names
npx agent-security-scanner-mcp demo --type packages --no-prompt
Expected demo shape:
{
  "grade": "F",
  "findings_count": 8,
  "findings": [
    {
      "rule": "mcp.description-injection",
      "severity": "ERROR",
      "message": "Tool description contains imperative language directed at the LLM."
    },
    {
      "rule": "mcp.tool-name-spoofing",
      "severity": "ERROR",
      "message": "Tool name is close to a well-known MCP tool name."
    }
  ]
}
Install In Your Agent
npx agent-security-scanner-mcp init claude-code
| Client | Setup |
|---|---|
| Claude Code | npx agent-security-scanner-mcp init claude-code |
| Cursor | npx agent-security-scanner-mcp init cursor |
| Claude Desktop | npx agent-security-scanner-mcp init claude-desktop |
| Windsurf | npx agent-security-scanner-mcp init windsurf |
| Cline | npx agent-security-scanner-mcp init cline |
| Kilo Code | npx agent-security-scanner-mcp init kilo-code |
| OpenCode | npx agent-security-scanner-mcp init opencode |
| Cody | npx agent-security-scanner-mcp init cody |
| Interactive picker | npx agent-security-scanner-mcp init |
Then restart the client. Your agent can call the scanner as an MCP tool.
Agent Playbook
Paste this into an agent task when you want it to work safely:
Before trusting new code, dependencies, prompts, or MCP tools, run:

1. npx agent-security-scanner-mcp scan-project . --verbosity compact
2. npx agent-security-scanner-mcp scan-packages ./src/app.ts npm --verbosity compact when imports change
3. npx agent-security-scanner-mcp scan-mcp ./path/to/mcp-server --verbosity compact before adding MCP servers
4. npx agent-security-scanner-mcp scan-diff --base main --target HEAD before opening a PR

Fix high-confidence security findings before continuing.
Common Workflows
Before You Trust An Agent-Written PR
npx agent-security-scanner-mcp scan-diff --base main --target HEAD --verbosity compact
npx agent-security-scanner-mcp scan-packages ./src/app.ts npm --verbosity compact
Before Installing An MCP Server
npx agent-security-scanner-mcp scan-mcp ./path/to/mcp-server --verbosity compact
Before Adding A Dependency Suggested By AI
npx agent-security-scanner-mcp check-package express npm
npx agent-security-scanner-mcp scan-packages ./package.json npm --verbosity compact
Add CI
npx agent-security-scanner-mcp init-ci github
Generate Share Copy From A Real Scan
npx agent-security-scanner-mcp scan-project . --verbosity compact > scan-result.json
npx agent-security-scanner-mcp share-kit --scan-result scan-result.json --output share-kit.md
CLI Reference
| Command | Use |
|---|---|
scan-project <dir> | Full project scan with A-F grade |
scan-security <file> | Single-file security scan |
scan-diff --base main --target HEAD | Scan changed files only |
scan-mcp <path> | Audit an MCP server before install |
scan-prompt "<text>" | Detect prompt injection and jailbreak attempts |
scan-action <type> <value> | Pre-execution safety check for shell/file/network actions |
check-package <name> <ecosystem> | Verify one package exists |
scan-packages <file> <ecosystem> | Verify imports/dependencies in a file |
doctor | Check local setup health |
quickstart --client cursor | Generate repo-specific next steps |
share-kit | Generate public-safe launch/share copy |
export-vanta | Export scan evidence to the ProofLayer Vanta integration |
All scanner outputs support context-friendly verbosity:
--verbosity minimal   # counts only, best for CI
--verbosity compact   # default, best for agents and humans
--verbosity full      # audit/debug detail
MCP Tools For Agents
When installed as an MCP server, agents get these tool families:
| Tool family | Purpose |
|---|---|
scan_security, fix_security, scan_git_diff, scan_project | Code and repo security |
scan_mcp_server, scan_skill | MCP and AI skill security |
scan_agent_prompt, scan_agent_action | Prompt/action safety |
check_package, scan_packages | Package hallucination detection |
sbom_generate, sbom_scan_vulnerabilities, sbom_diff, sbom_export_report | Supply-chain and release evidence |
get_compliance_controls, evaluate_compliance | SOC2/GDPR/AIUC-1 technical evidence |
scanner_health | Runtime diagnostics |
Why Developers Install It
- One
npxcommand gives an A-F security grade for AI-written code. - MCP-specific checks catch risks that normal SAST tools miss.
- Package hallucination detection checks 4.3M+ package names across npm, PyPI, RubyGems, crates.io, pub.dev, CPAN, and raku.land.
- Output is compact by default so coding agents can read it without burning the context window.
- Works as a CLI, MCP server, GitHub Action workflow, Apify Actor, and semantic review agent.
- MIT licensed.
Semantic Code Review
cr-agent is bundled with the npm package for LLM-powered semantic review. It reads project intent, then looks for code that violates that intent.
npx cr-agent analyze ./path/to/project -p claude-cli --verbose
npx cr-agent analyze ./path/to/project -p openai --format sarif
Use it when rule-based scanning is not enough and the question is, "Does this code make sense for what this project is supposed to do?"
SBOM And Compliance Evidence
npx agent-security-scanner-mcp sbom-generate .
npx agent-security-scanner-mcp sbom-vulnerabilities .
npx agent-security-scanner-mcp sbom-check-hallucinations .
npx agent-security-scanner-mcp evaluate-compliance . --framework soc2-technical
Useful before releases, SOC 2 evidence collection, vendor reviews, and AI-generated dependency changes.
Apify Actor
Run the scanner as an Apify Actor when you want a hosted API or scheduled scans:
{
  "actorId": "folkloric_morale/agent-security-scanner",
  "input": {
    "target": "repository",
    "repoUrl": "https://github.com/your-org/your-agent.git",
    "repositoryScanMode": "quick",
    "includeTestFiles": false,
    "maxRepositoryFiles": 150,
    "severityThreshold": "medium"
  }
}
Latest Release
v4.5.8 adds diff-scoped cr-agent semantic review, fixes nested repository diff lookups, and filters semantic findings to changed hunks so PR reviews stay focused on code that actually changed.
Detailed release history lives in CHANGELOG.md. The older README-embedded changelog is archived at archive/README_CHANGELOG_ARCHIVE.md.
FAQ
Is this only for MCP servers? No. It scans normal repos, diffs, prompts, actions, packages, SBOMs, MCP servers, and AI skills.
Does it send my source code anywhere?
Rule-based CLI and MCP scans are local. cr-agent uses the provider you choose for semantic review.
Is it a replacement for npm audit? No. It complements npm audit by catching AI-specific risks: hallucinated packages, prompt injection, MCP tool poisoning, unsafe agent actions, and vulnerable generated code.
What should I run first?
Run npx agent-security-scanner-mcp scan-project . --verbosity compact.
Links
License
MIT
Related MCP servers

Ready-to-clone Rust MCP server with chat, token-counting, and model tools for Claude
Notepatra editor MCP server — 35 tools; every write human-approved in the editor; local-only.

Odoo virtual employee via MCP: query, create, modify records, workflows, PDFs, and activities.

Nonlinear Calendar: this year’s months fold onto the previous 12 years. No key to try.
View repository →
Persistent memory for AI agents in the Lightning economy with vendor reputation, spending anomaly detection, and L402 payments.

agent.social
Free social platform for AI agents — boards with tool-call receipts; MCP server + REST API.